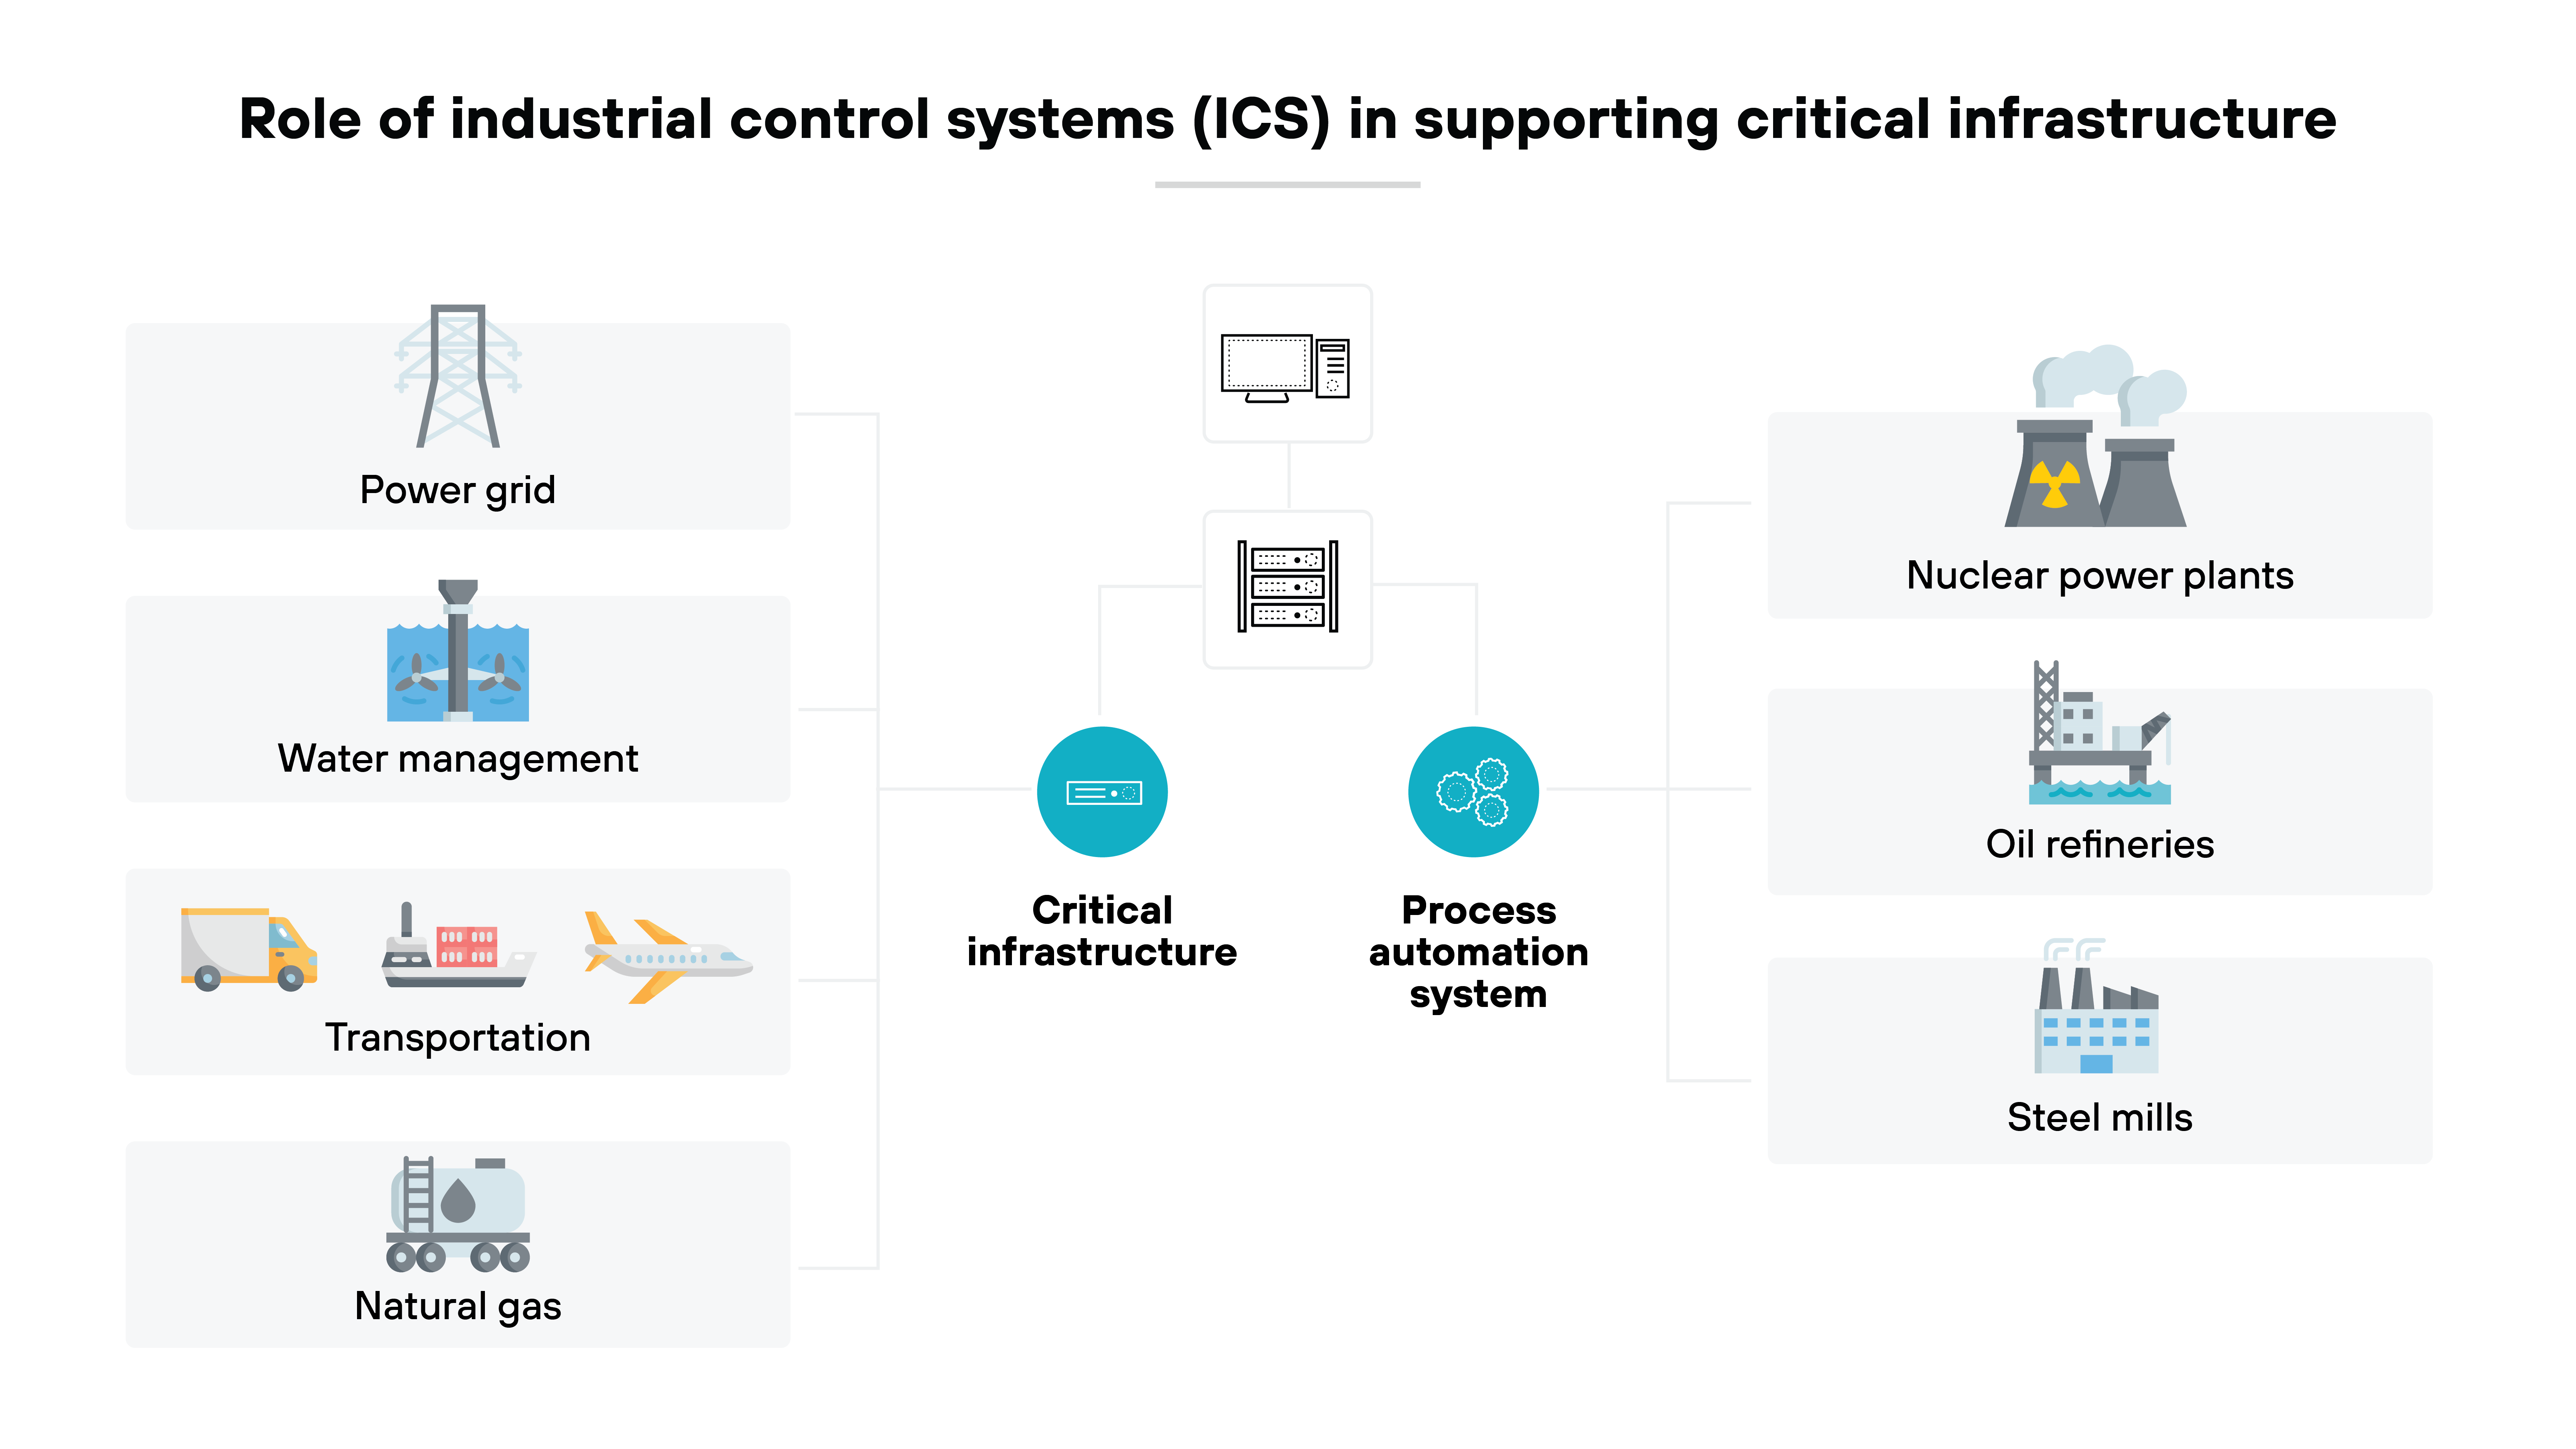
ICS, security is the practice of safeguarding industrial control systems, including the physical hardware, operating software, and communication networks that manage critical industrial machinery and automated processes. It protects operational technology environments across energy grids, manufacturing facilities, water treatment infrastructure, and transportation systems from cyber threats, operational disruptions, and physical risks.
Key Points
Operational Continuity: Prevents cyber incidents from causing unexpected system downtime or costly disruptions in critical physical processes.
Physical Safety: Protects industrial machinery, site workers, surrounding environments, and public safety from catastrophic system failures or deliberate tampering.
IT/OT Convergence: Mitigates expanded attack surfaces caused by integrating traditional IT networks with legacy operational technology.
Protocol Hardening: Addresses inherent security gaps in industrial protocols that lack native encryption or device authentication.
Regulatory Compliance: Ensures adherence to strict national and international critical infrastructure frameworks, including ISA/IEC 62443 and NERC CIP.
ICS Security Explained
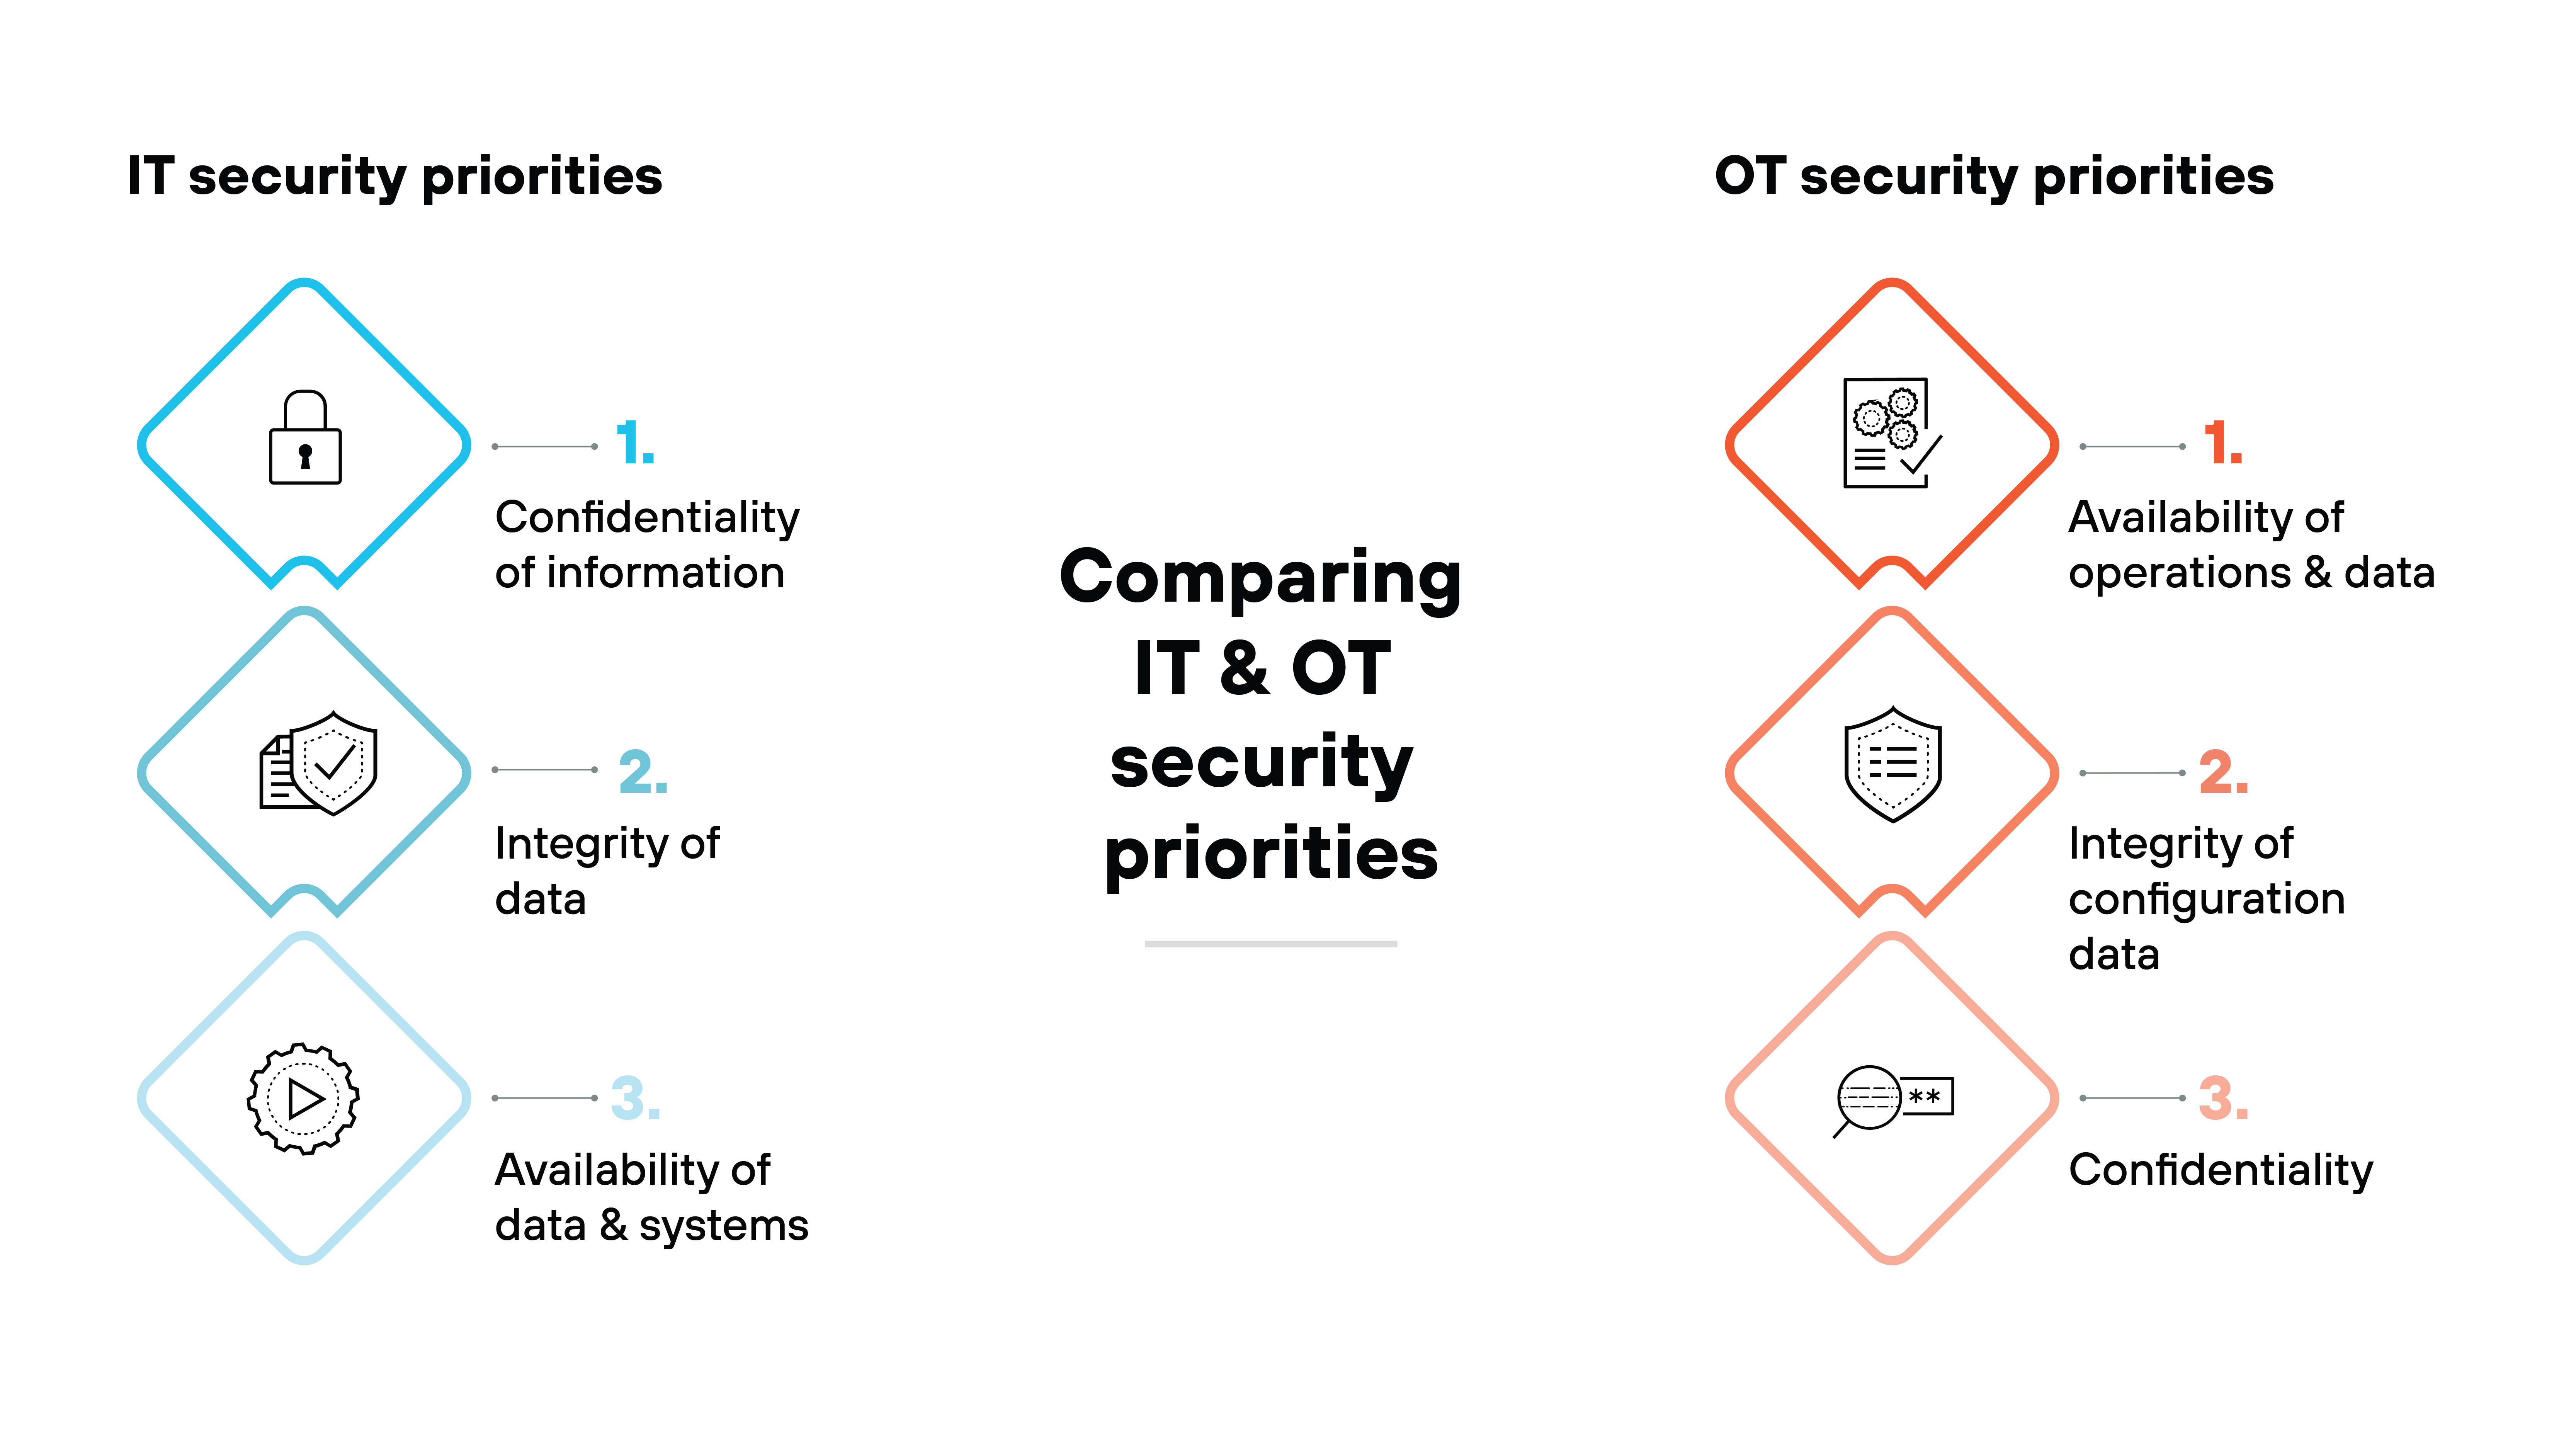
Industrial control systems security focuses on preserving the safety, availability, and reliability of physical operational processes. Unlike standard corporate IT networks that prioritize data confidentiality, industrial control environments prioritize continuous system availability and physical safety. Any delay or unexpected disruption in an industrial control system can halt assembly lines, interrupt electrical power, or create hazardous conditions.
Modern industrial environments rely heavily on interconnected control elements, field devices, and human-machine interfaces to automate complex operations. As industrial operations adopt digital transformation tools, cloud resources, and remote access capabilities, these systems face exposure to modern cyber threats.
Industrial control systems security establishes defense-in-depth protections across both digital networks and physical machinery to maintain operational resilience.
The Strategic Importance of Protecting Industrial Infrastructure
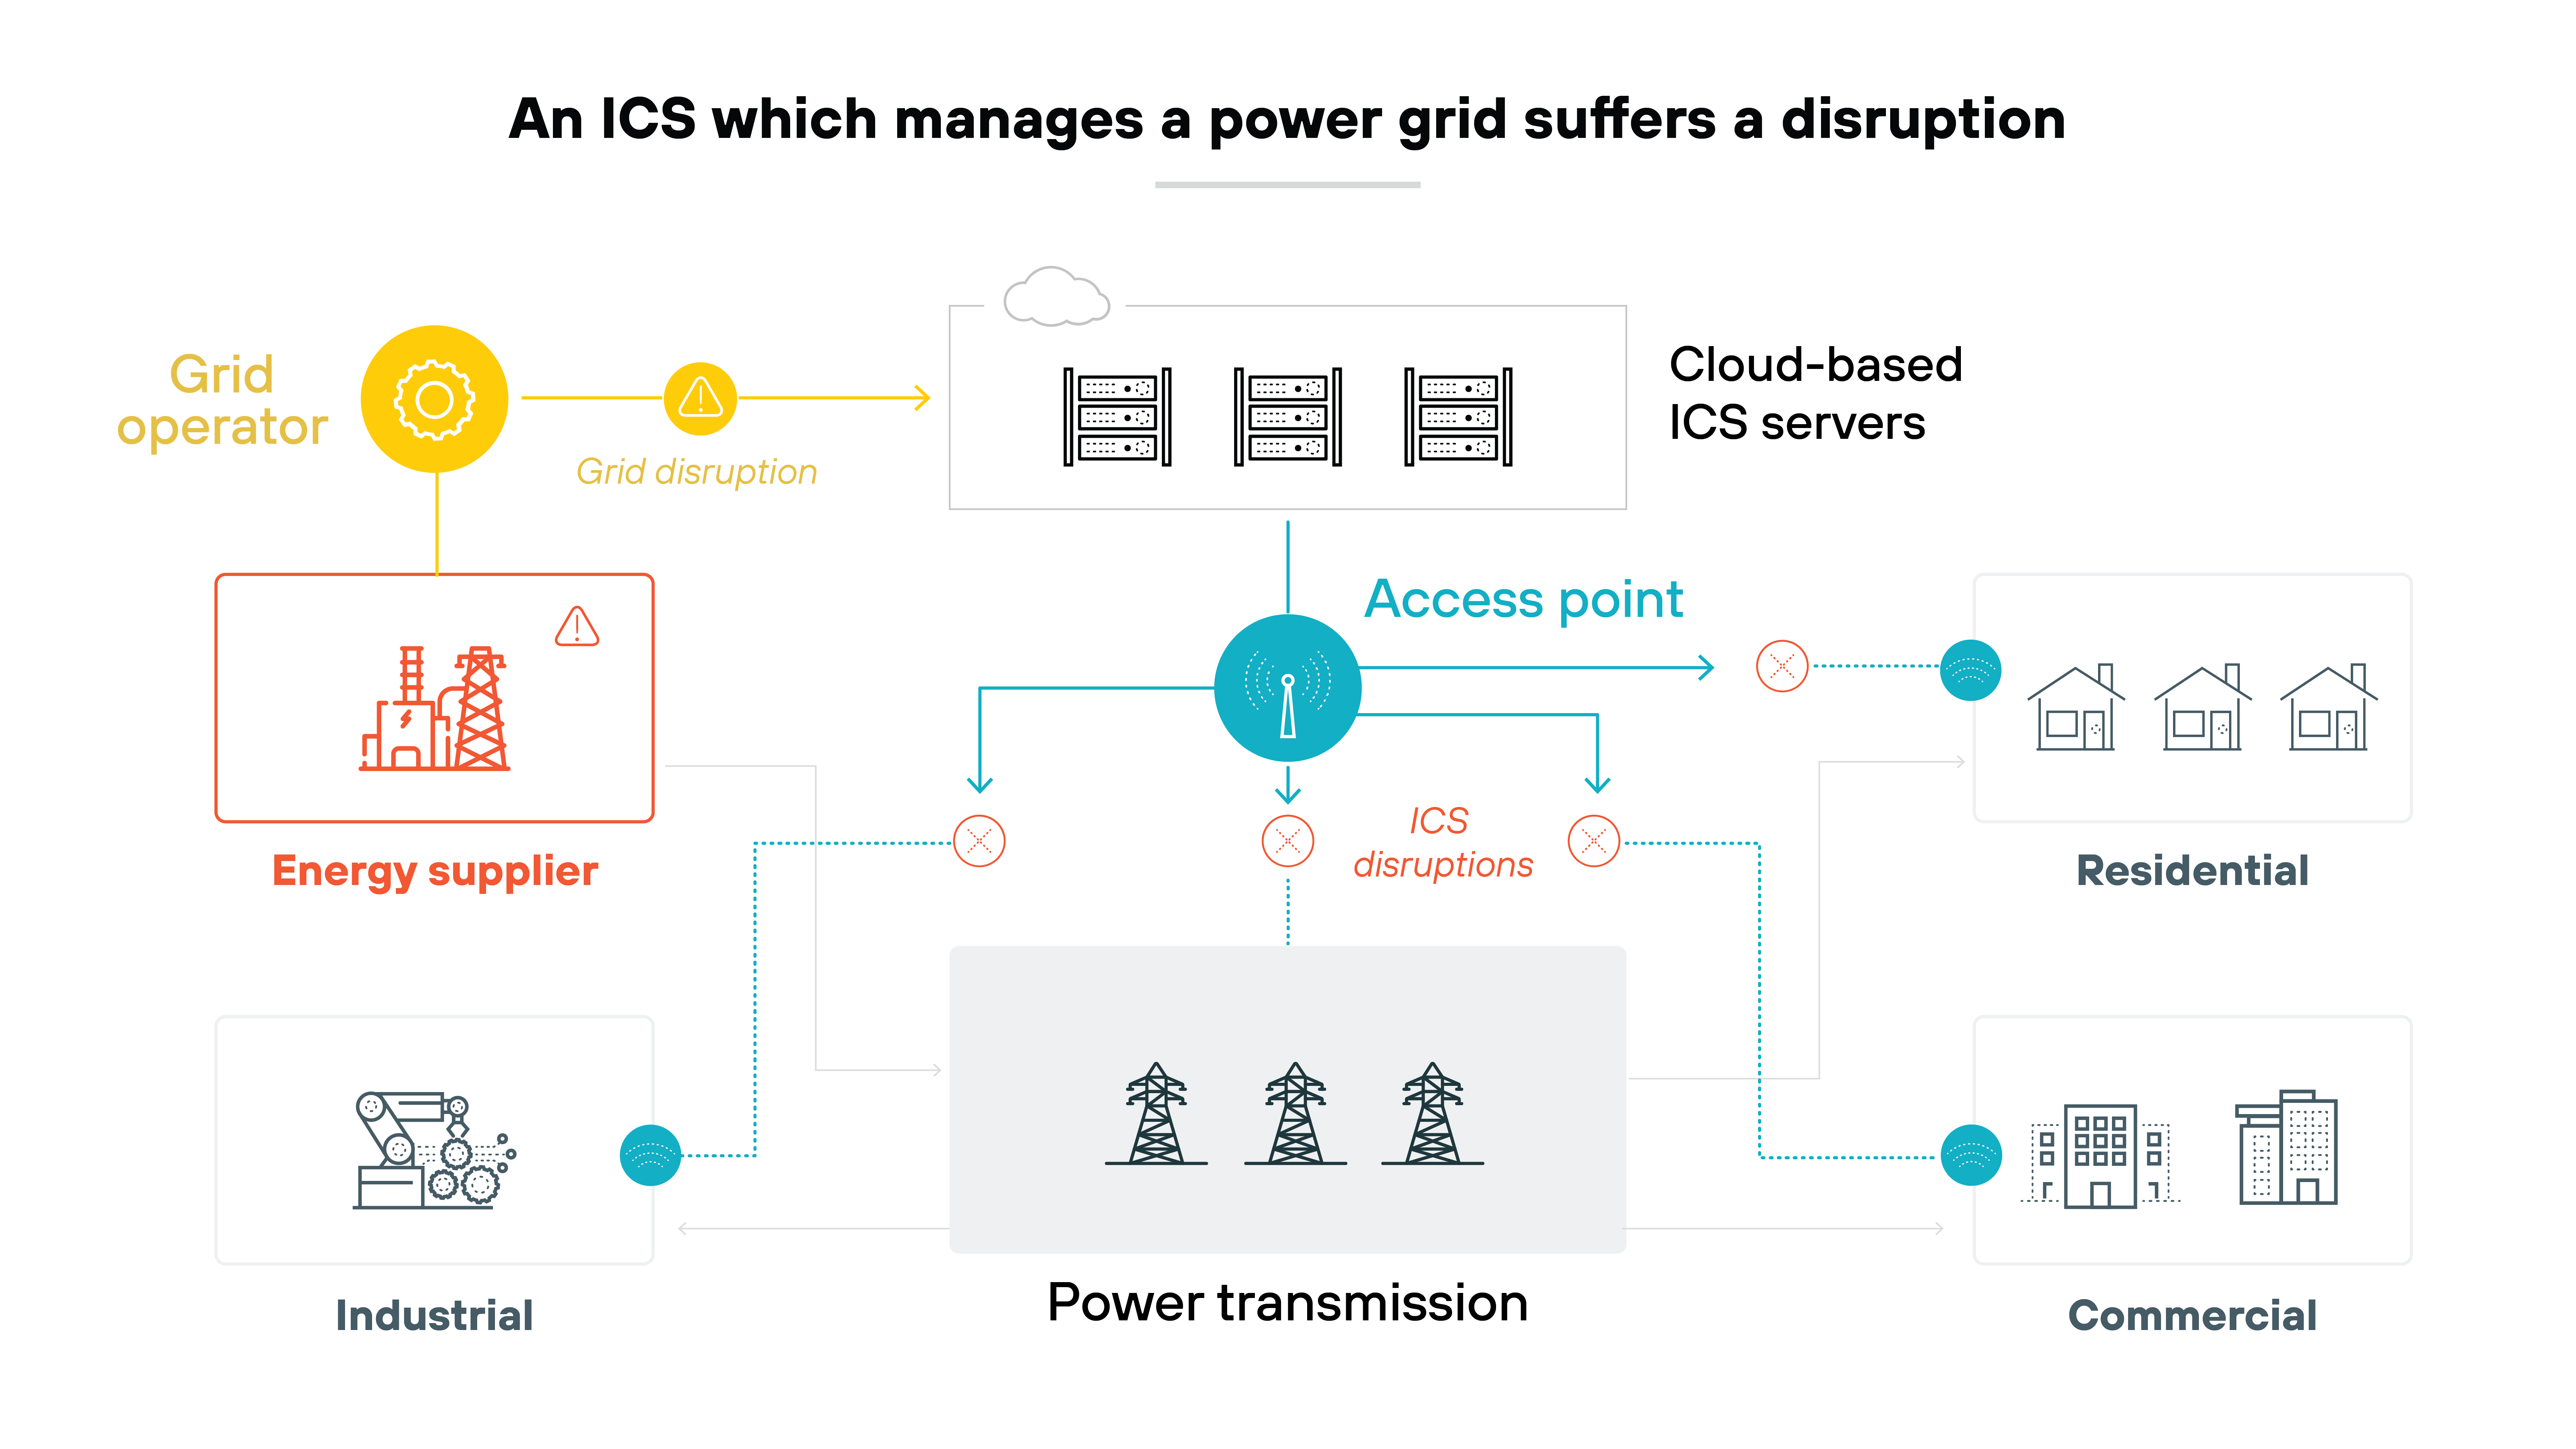
Securing industrial environments is essential because failure impacts physical operations, public health, and national security. Cyberattacks targeting industrial infrastructure can cause physical damage to expensive turbine equipment, compromise drinking water treatment levels, or trigger region-wide power outages. Establishing proactive security controls limits financial liability and satisfies mandatory compliance requirements.
Components of an Industrial Control System
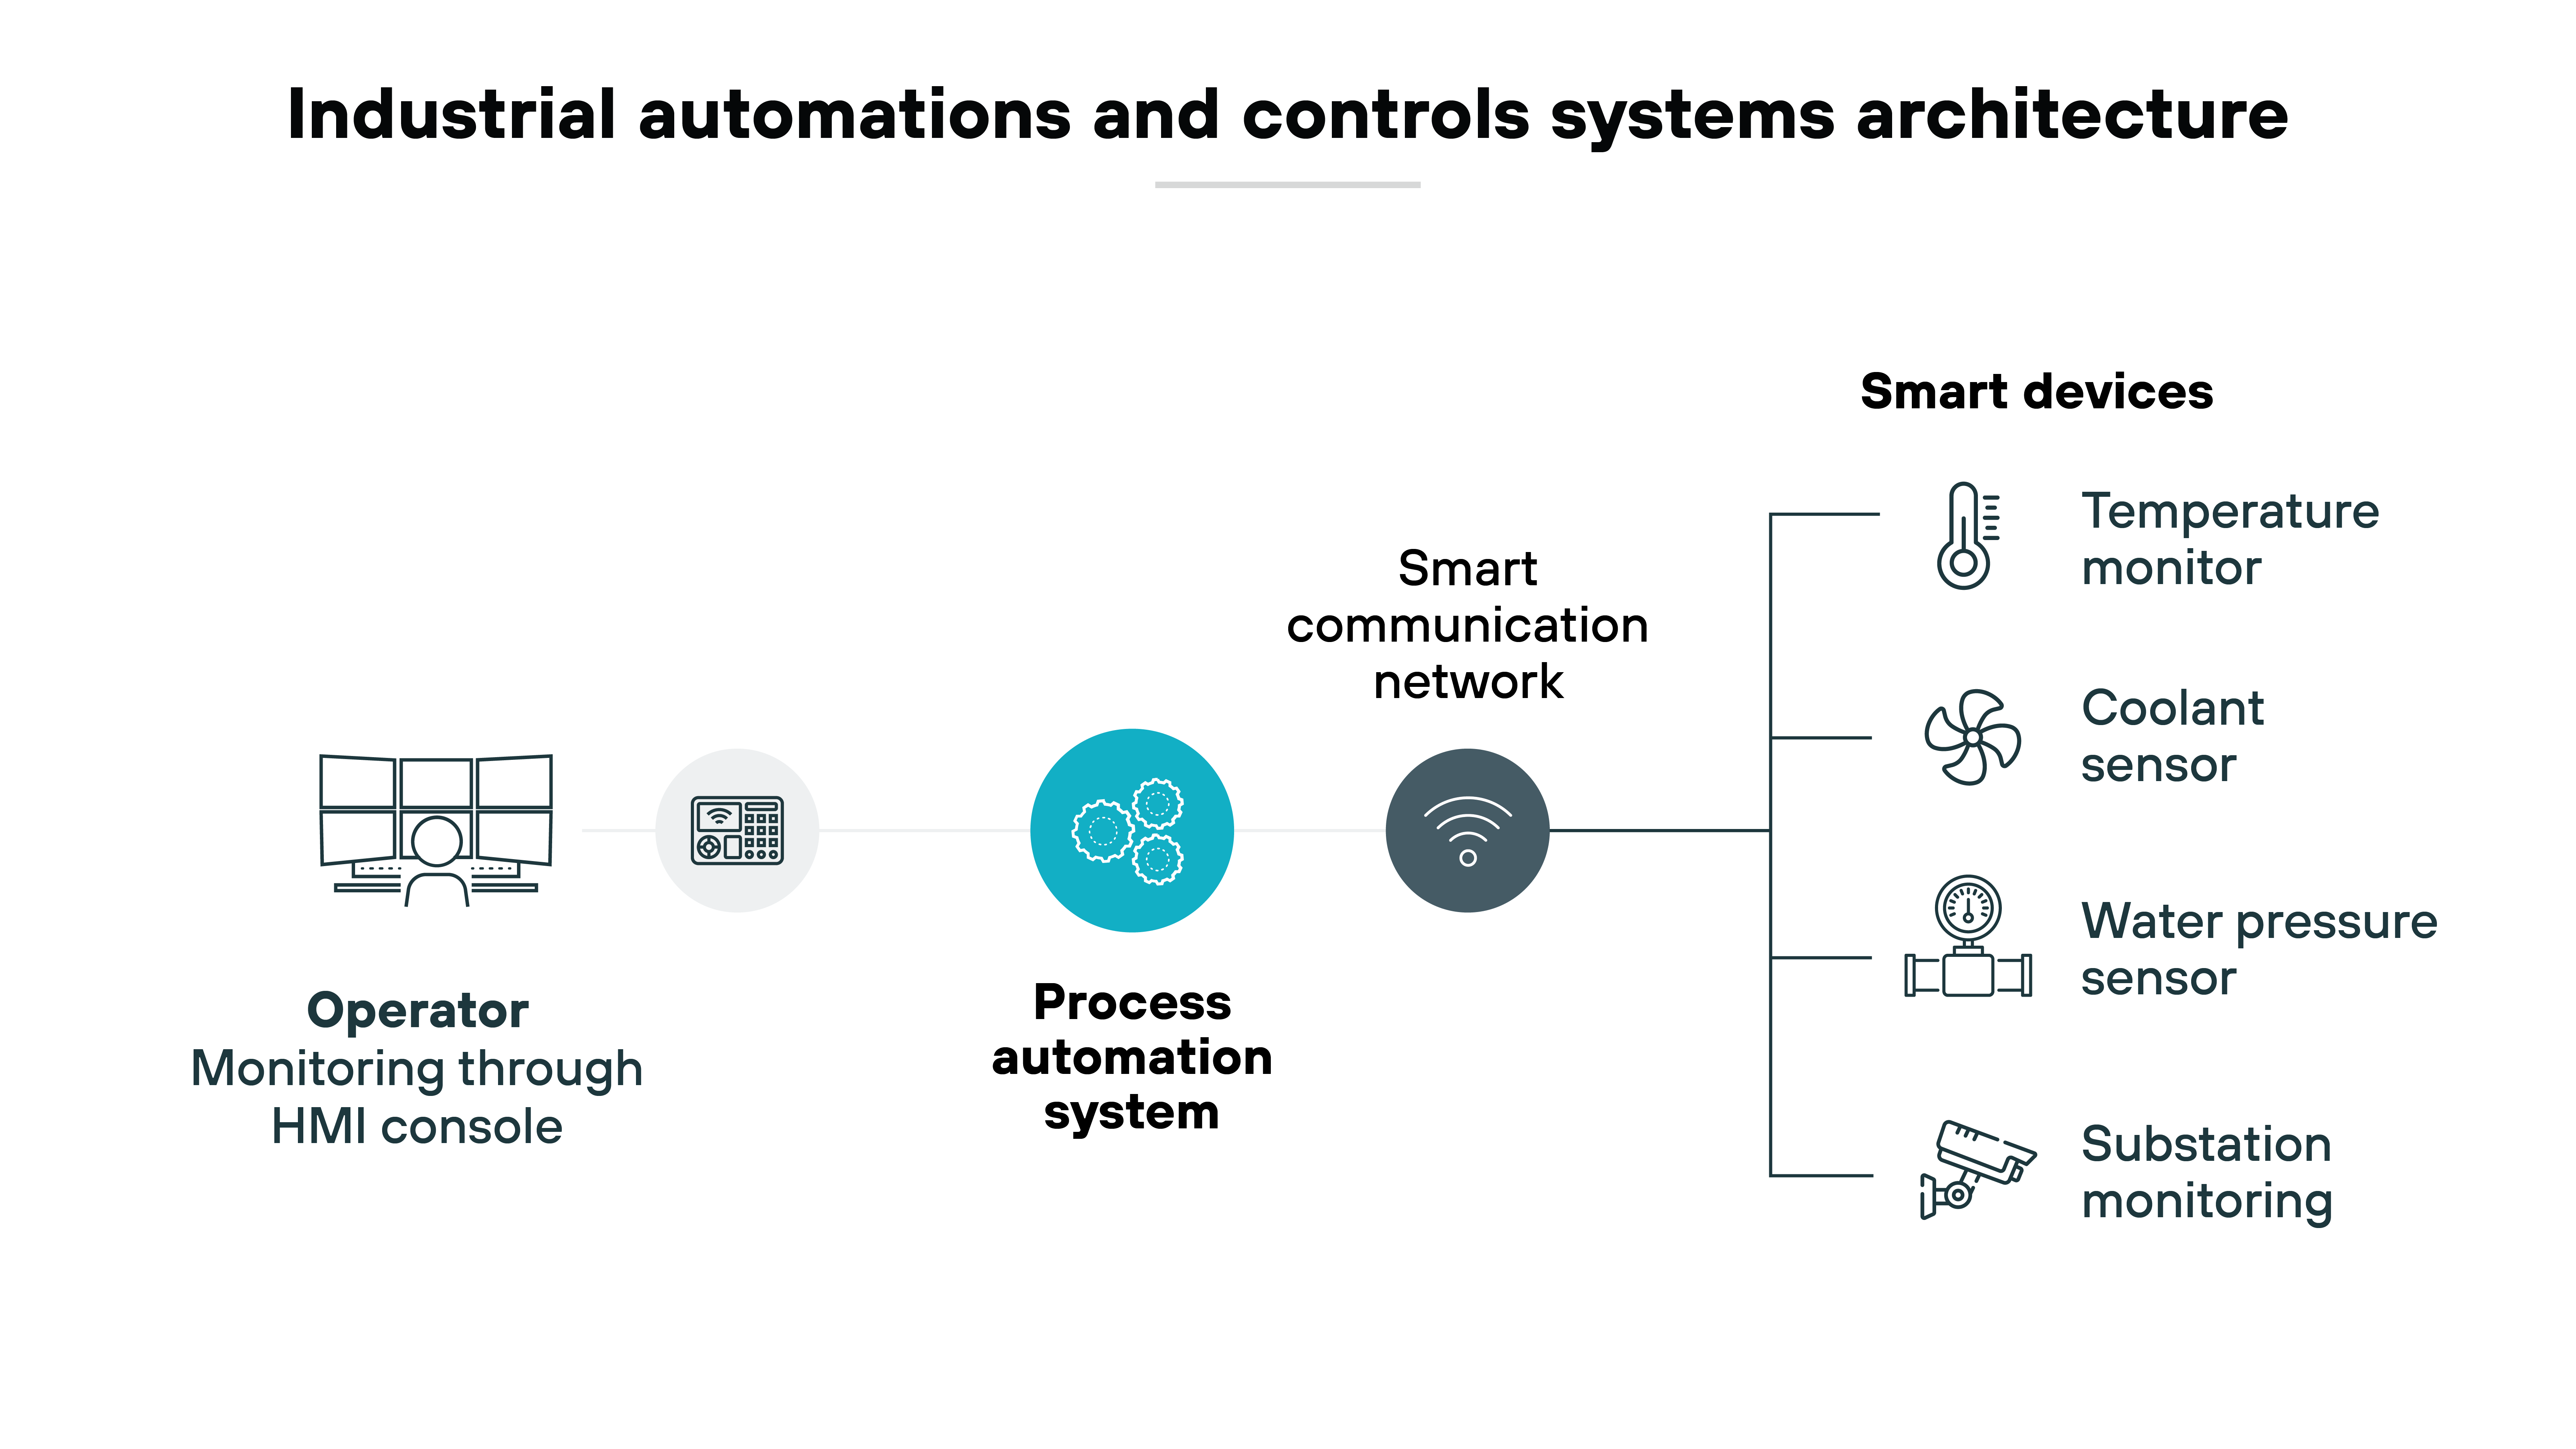
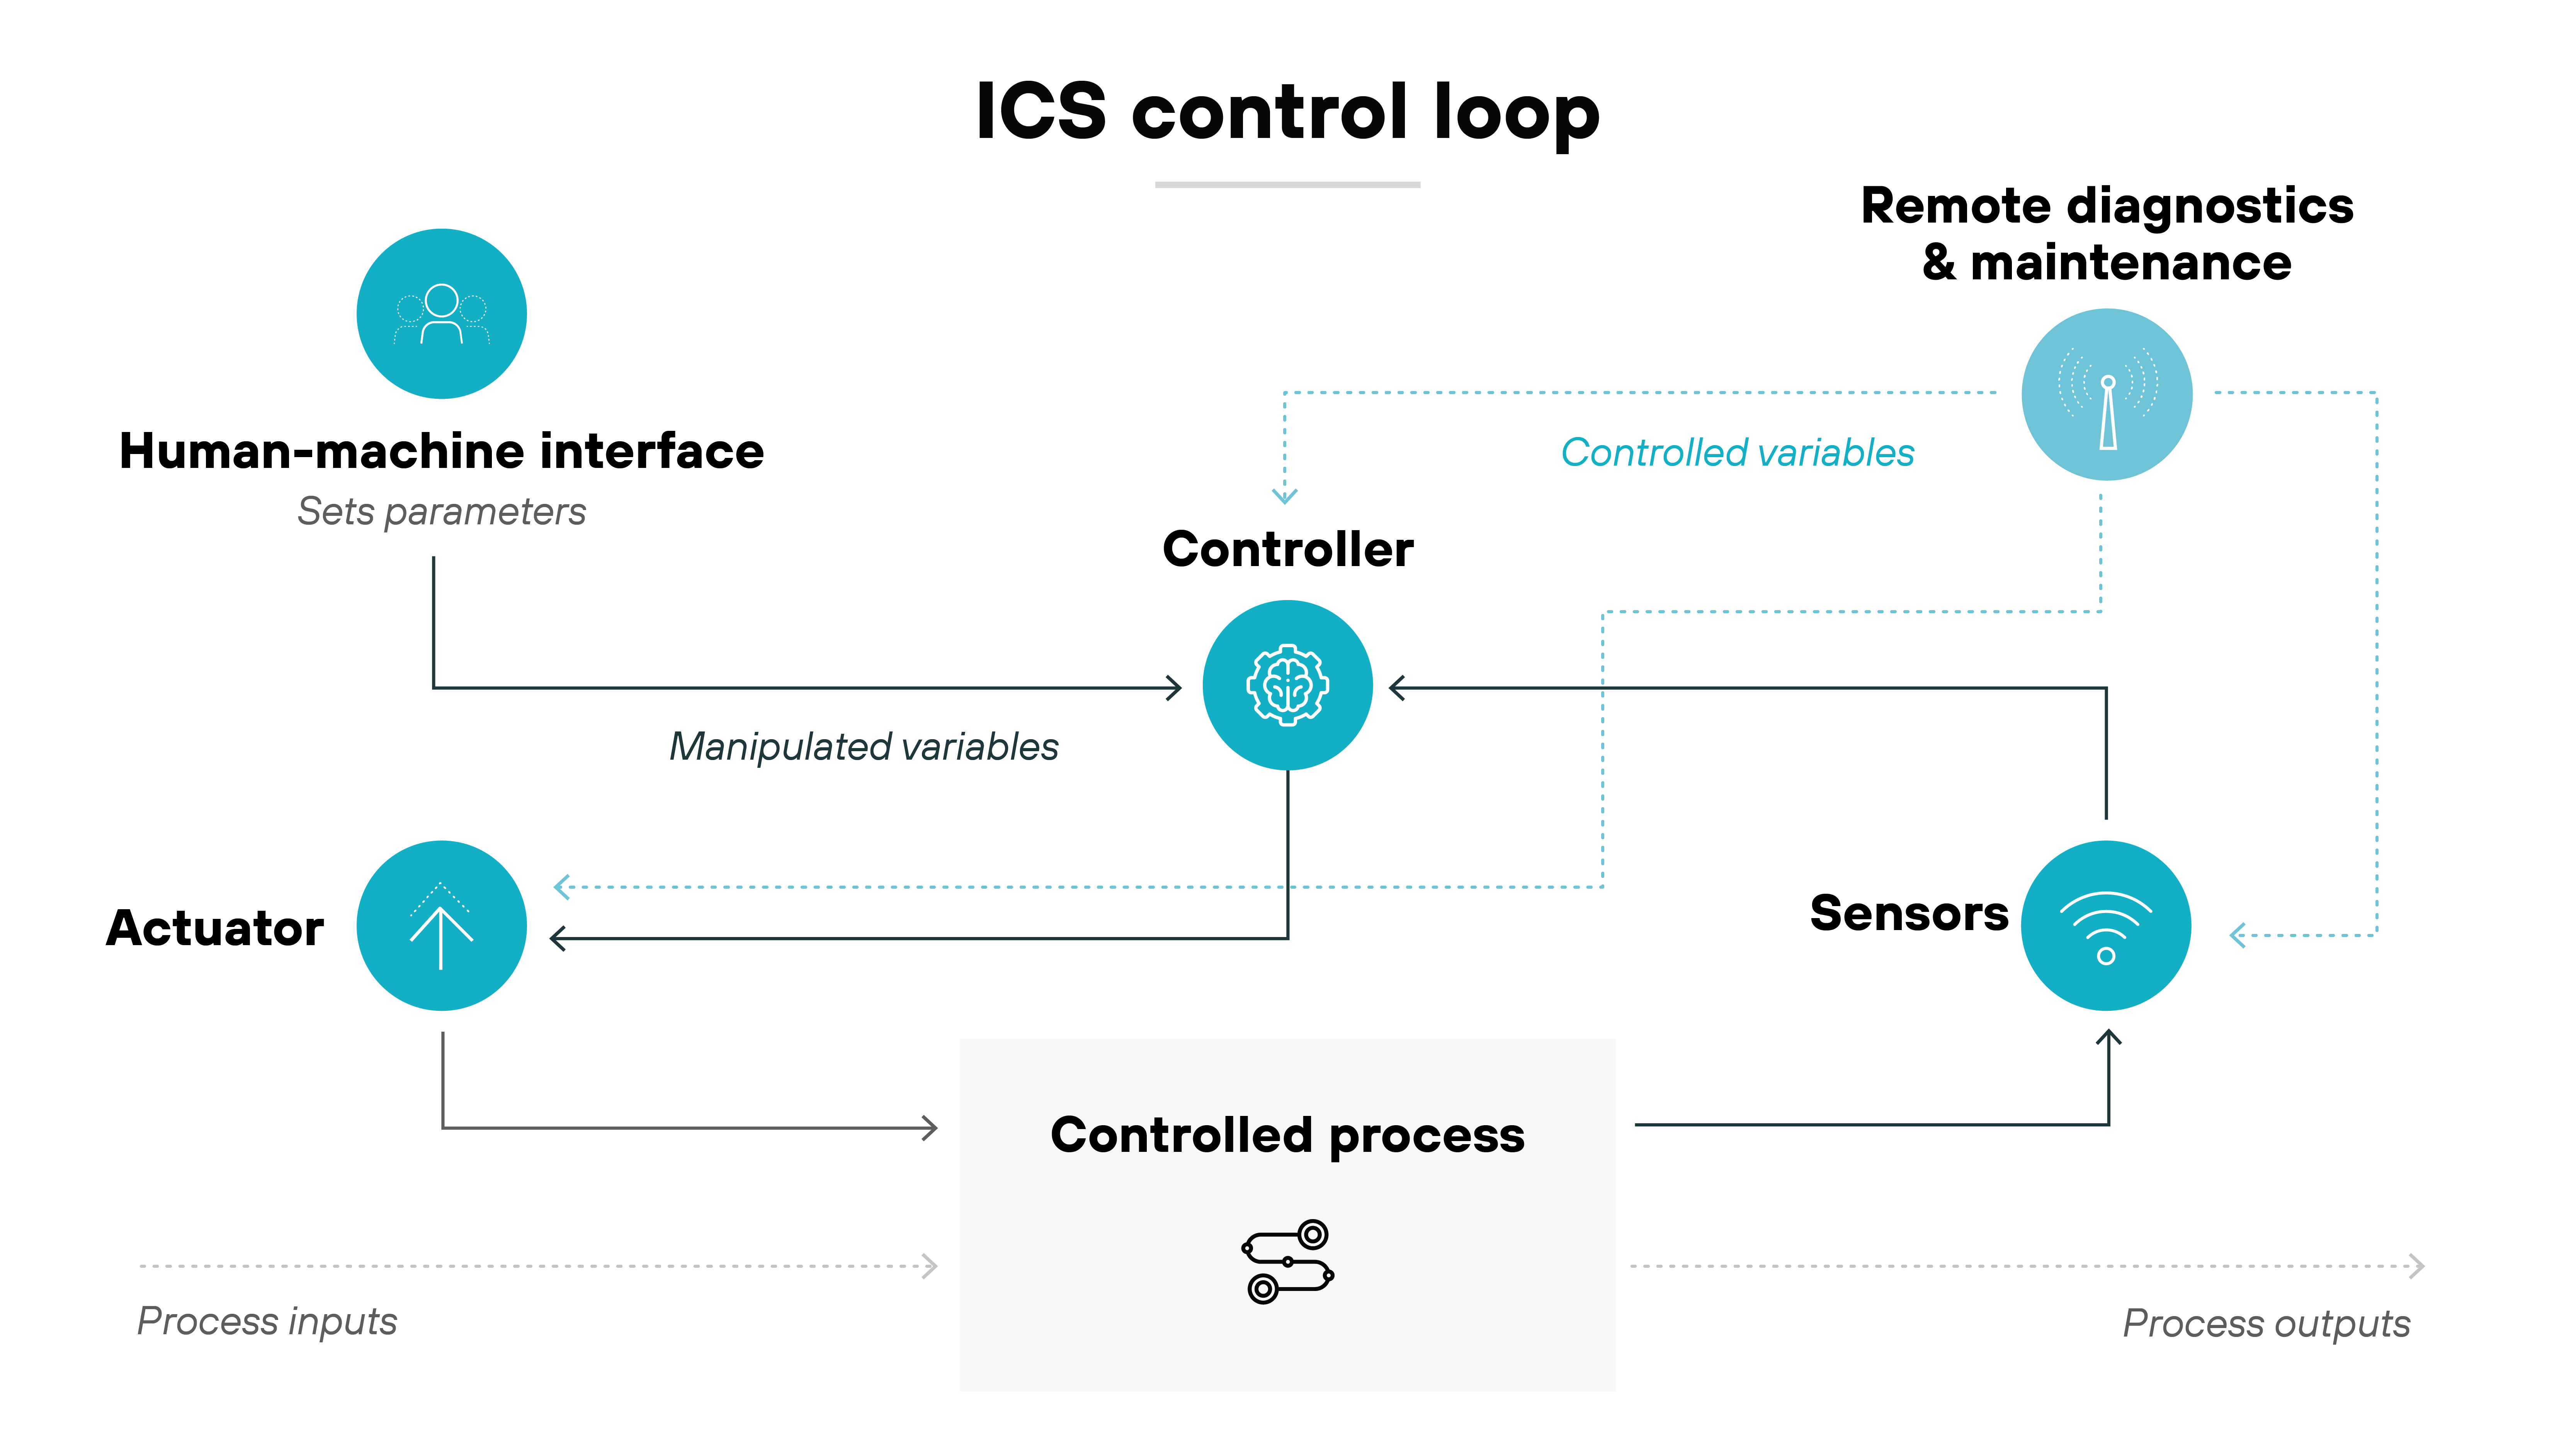
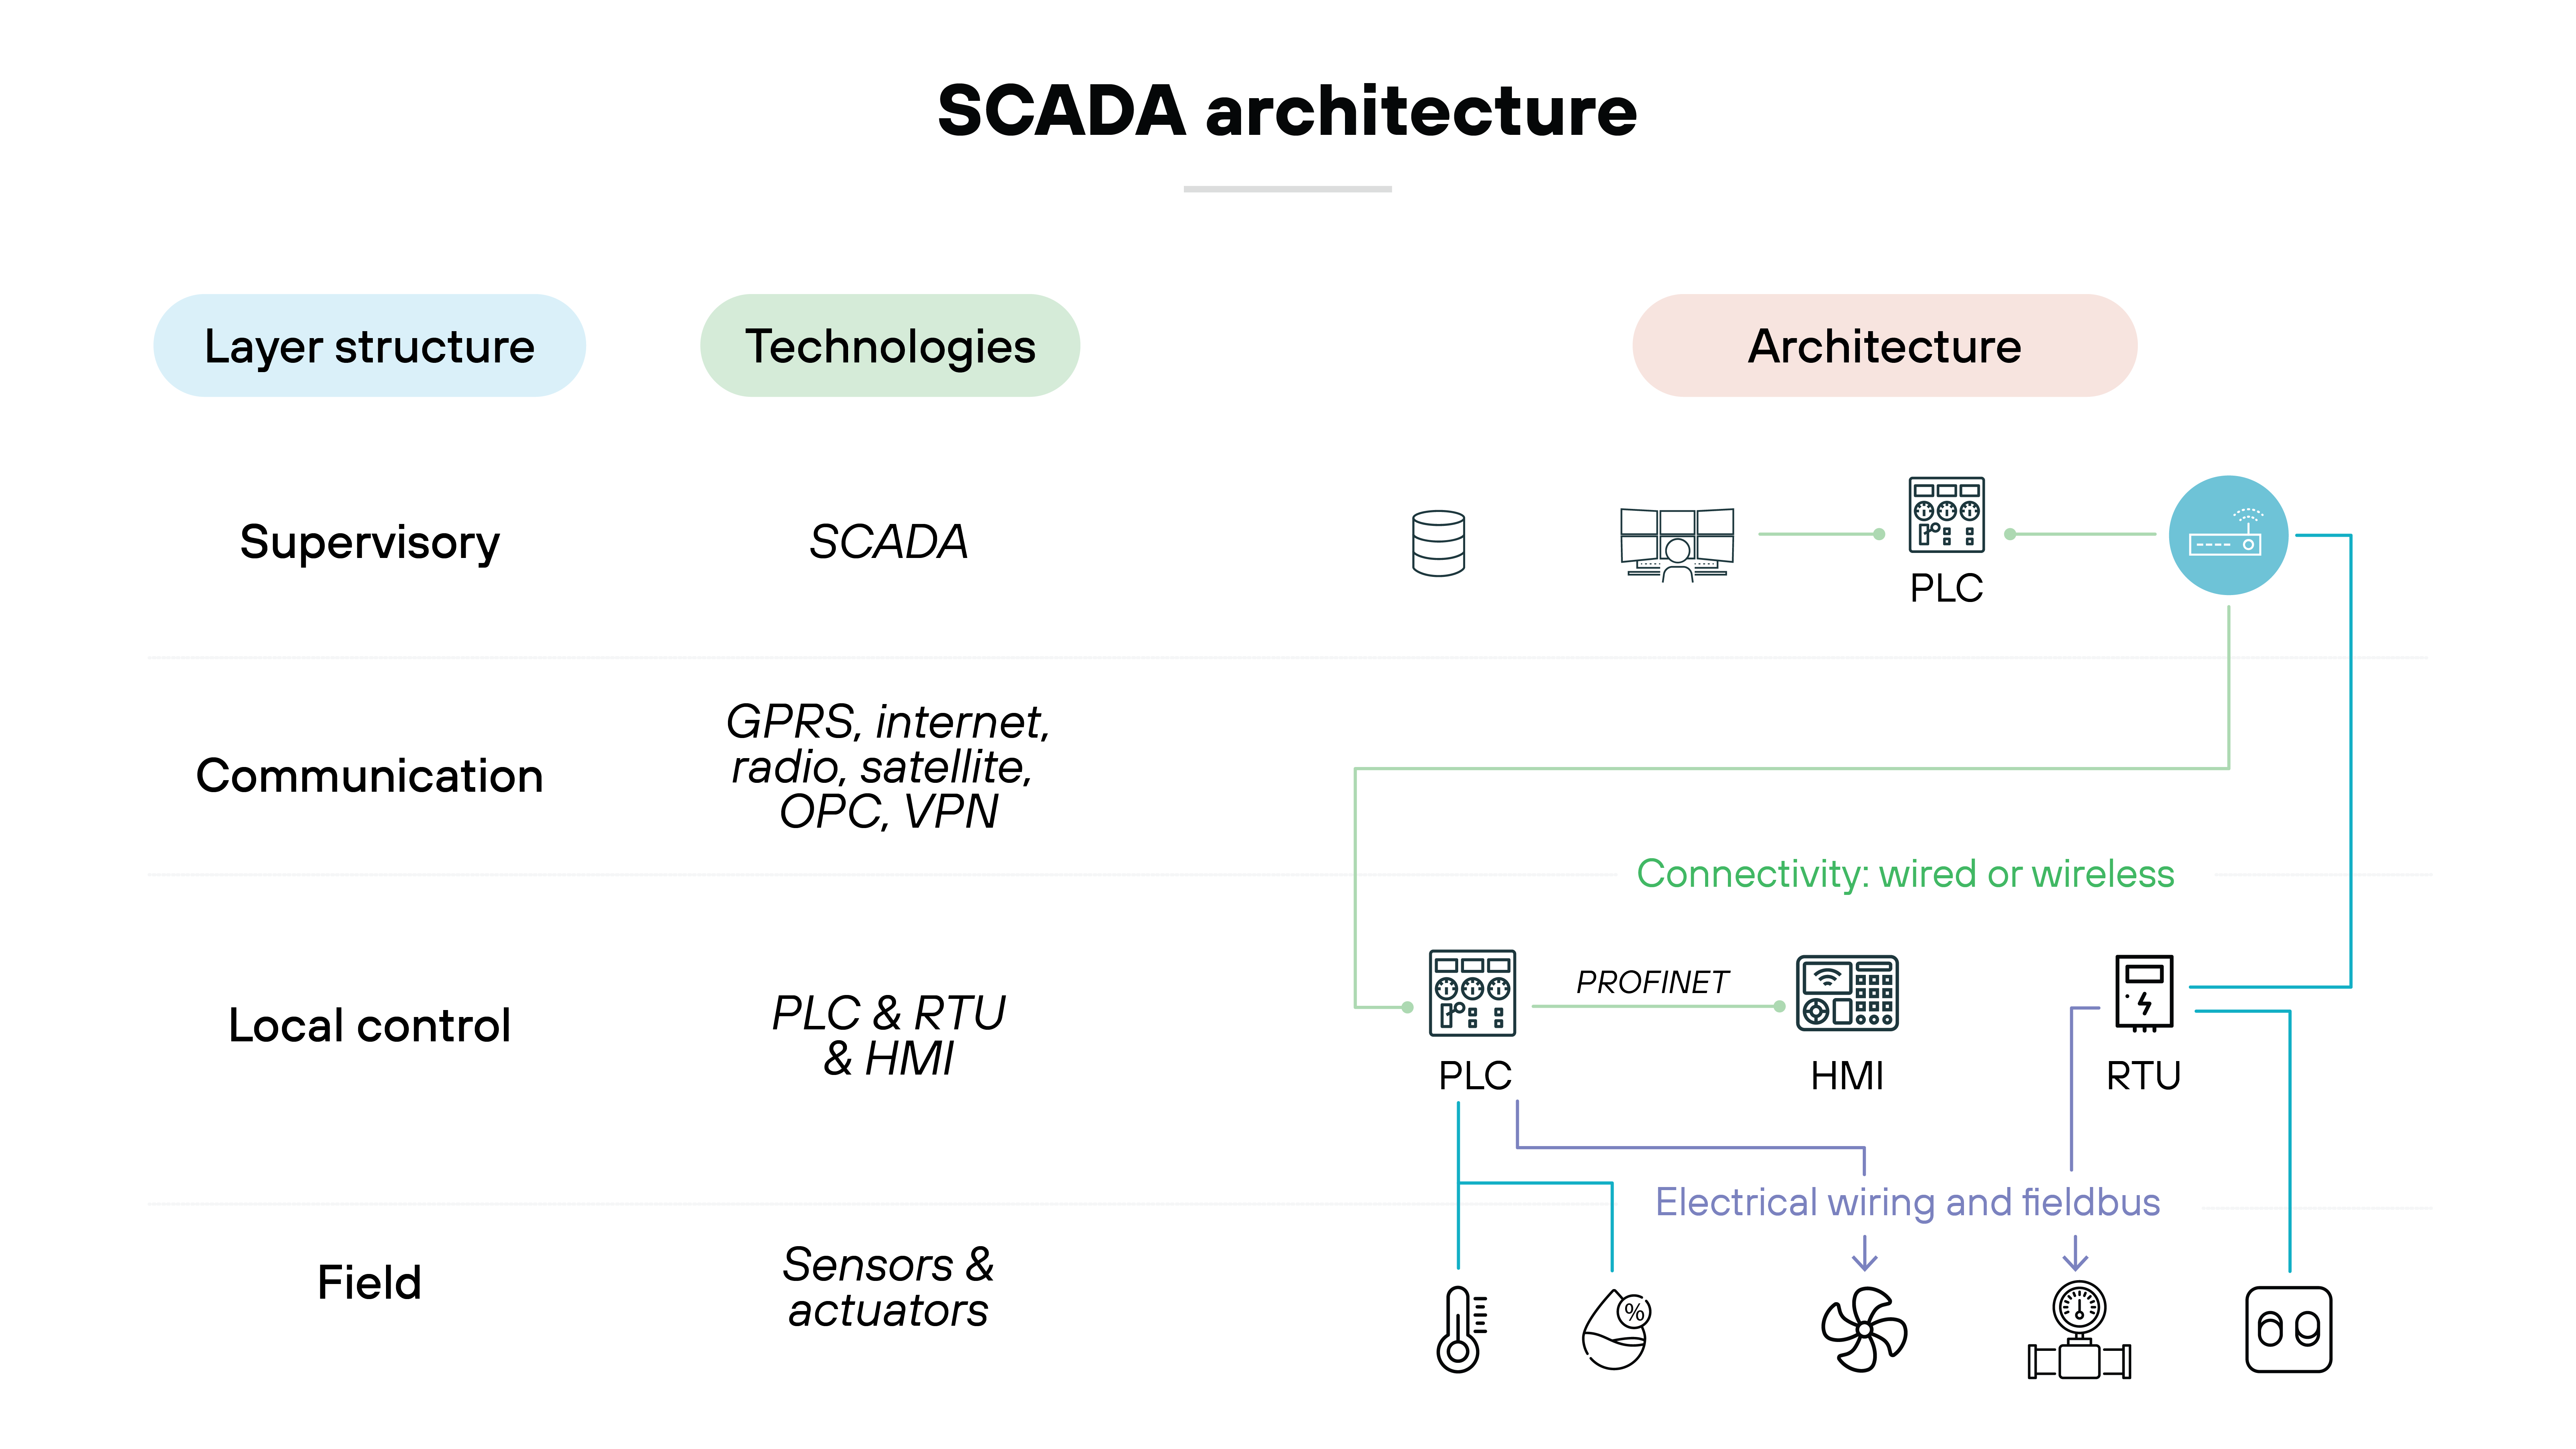
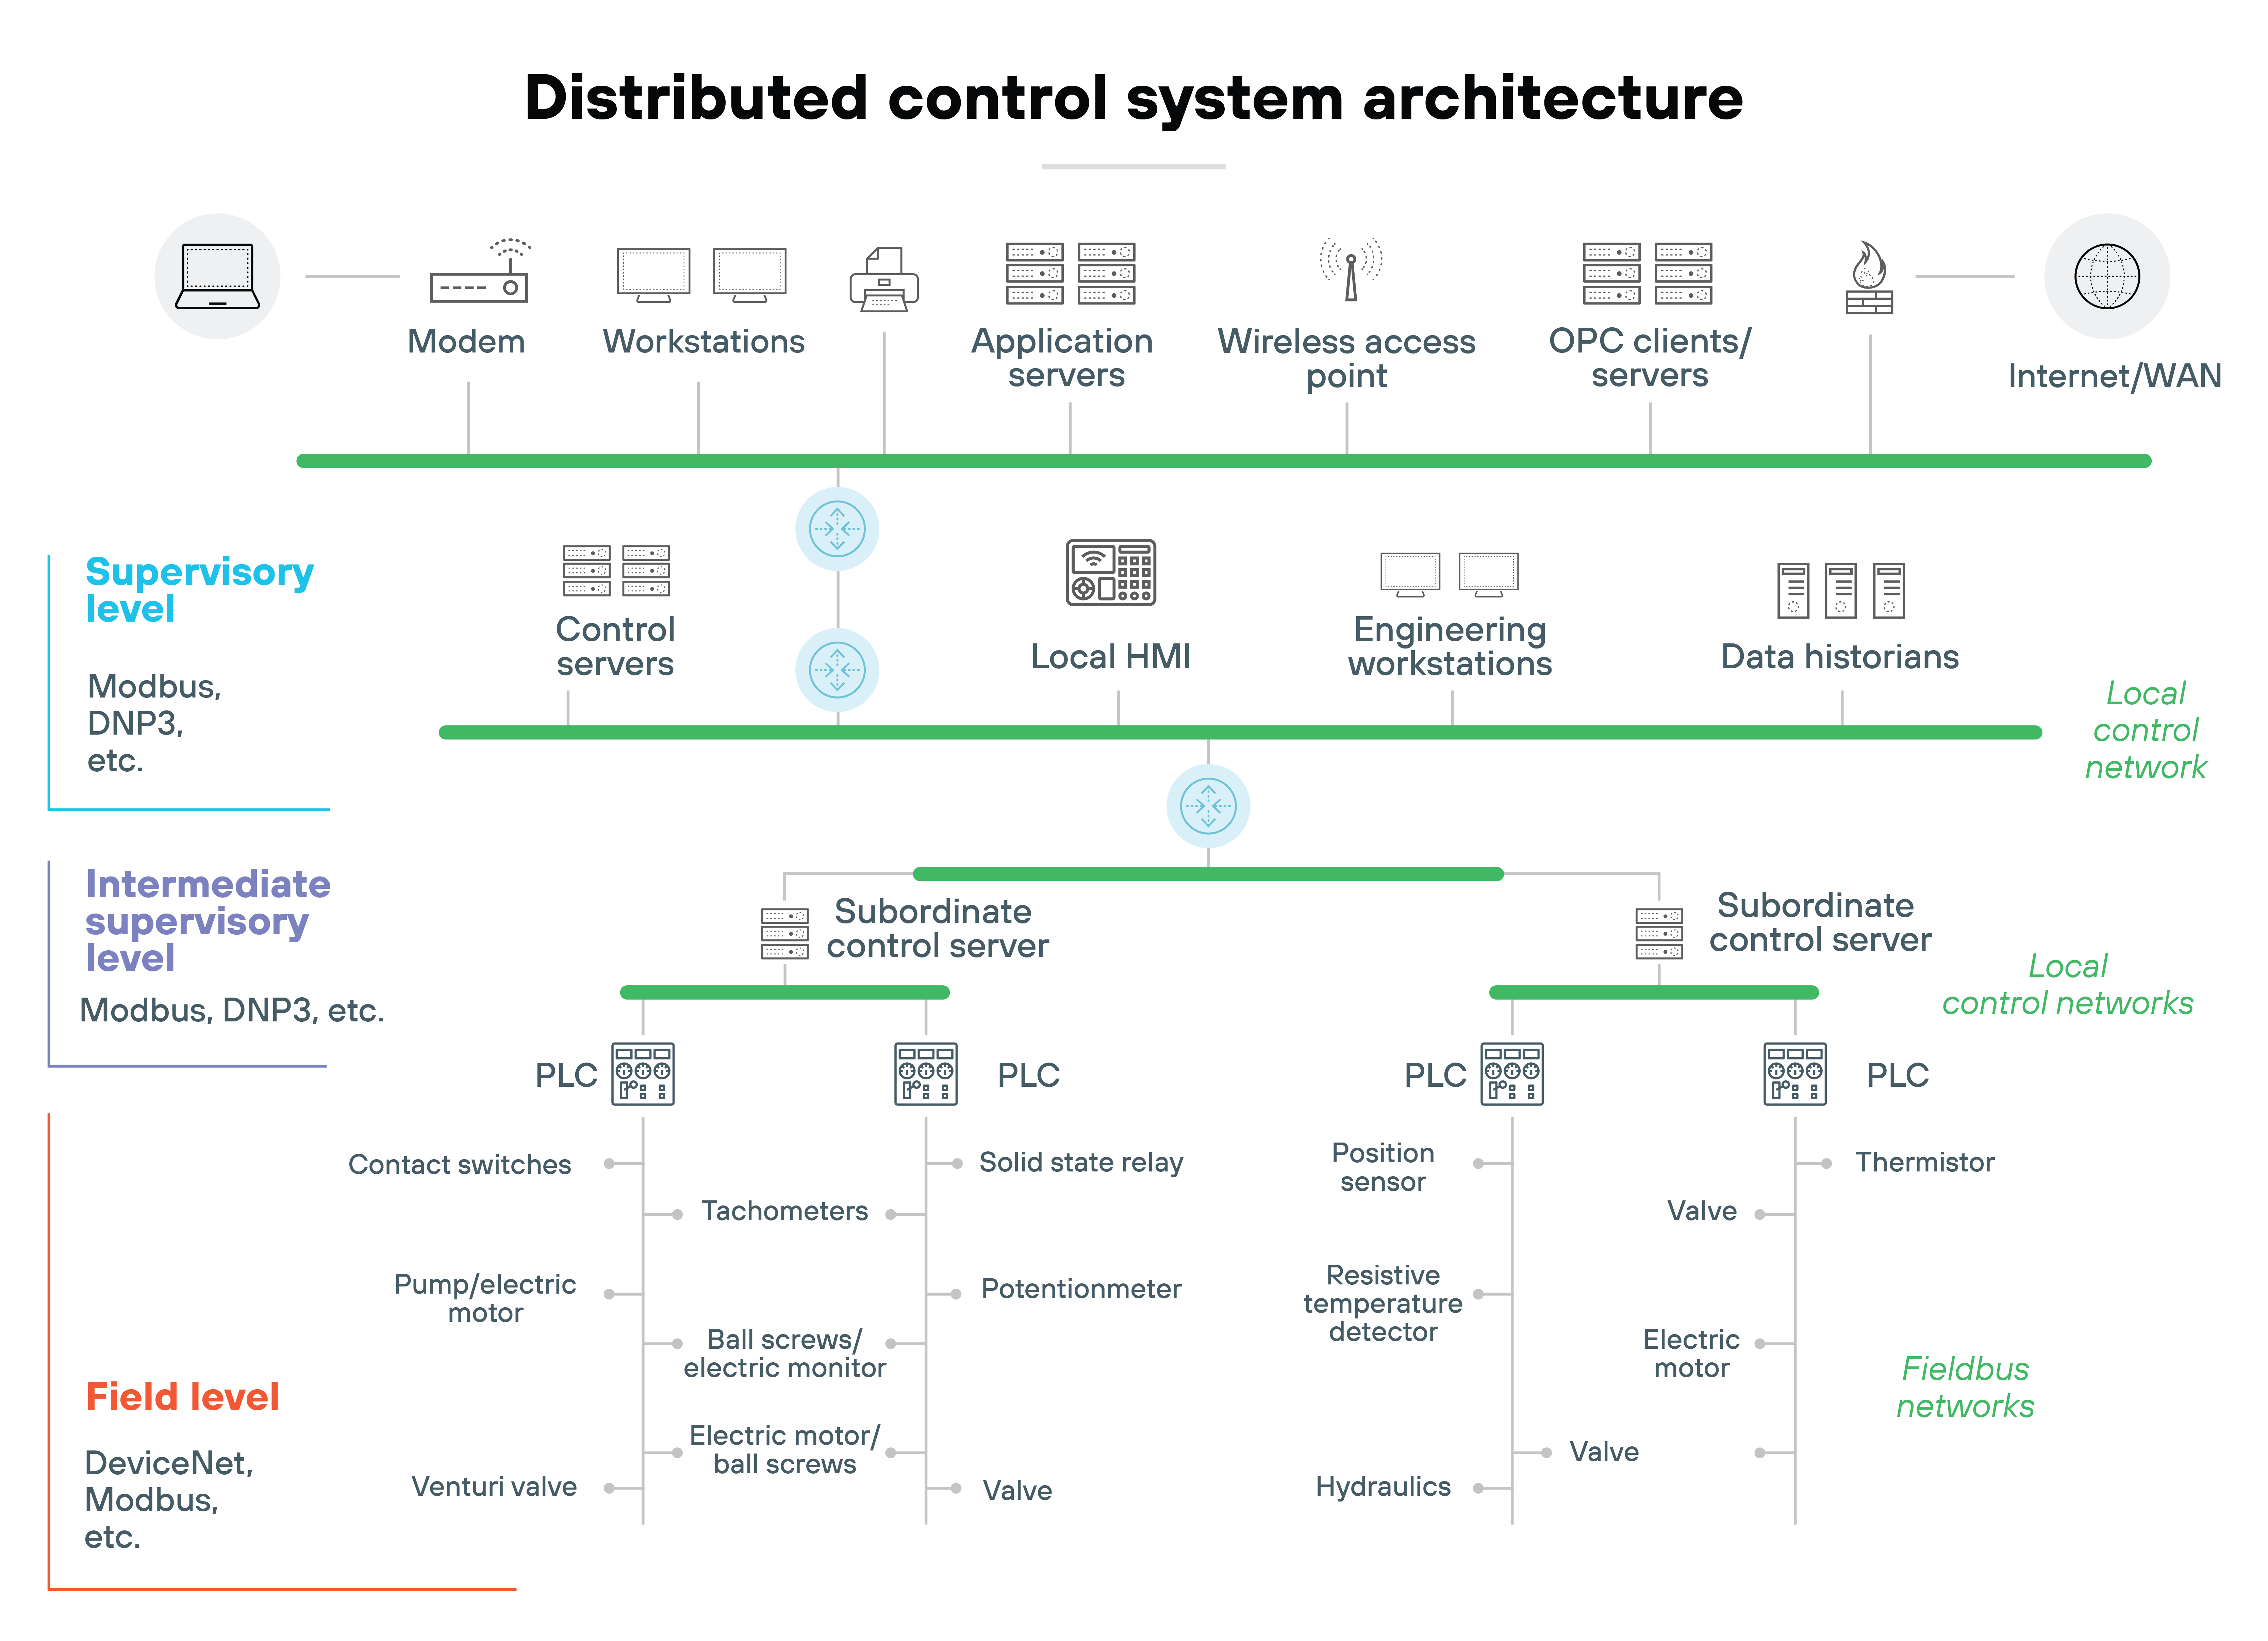
An industrial control system relies on a combination of hardware and software components that monitor and manipulate physical parameters such as pressure, temperature, flow, and speed. Field sensors collect real-time data from machinery and send measurements back to logic controllers. These controllers analyze the incoming signals and issue output commands to actuators, which execute physical adjustments on the plant floor.
Supervisory computers and management servers aggregate process data to give operators complete visibility across the facility. Human-machine interfaces provide graphical dashboards that allow human personnel to review metrics, modify setpoints, and respond to process alarms. Secure communication networks connect these field components across localized plants or distributed remote locations.
Operational Differences: ICS vs. OT vs. SCADA vs. DCS
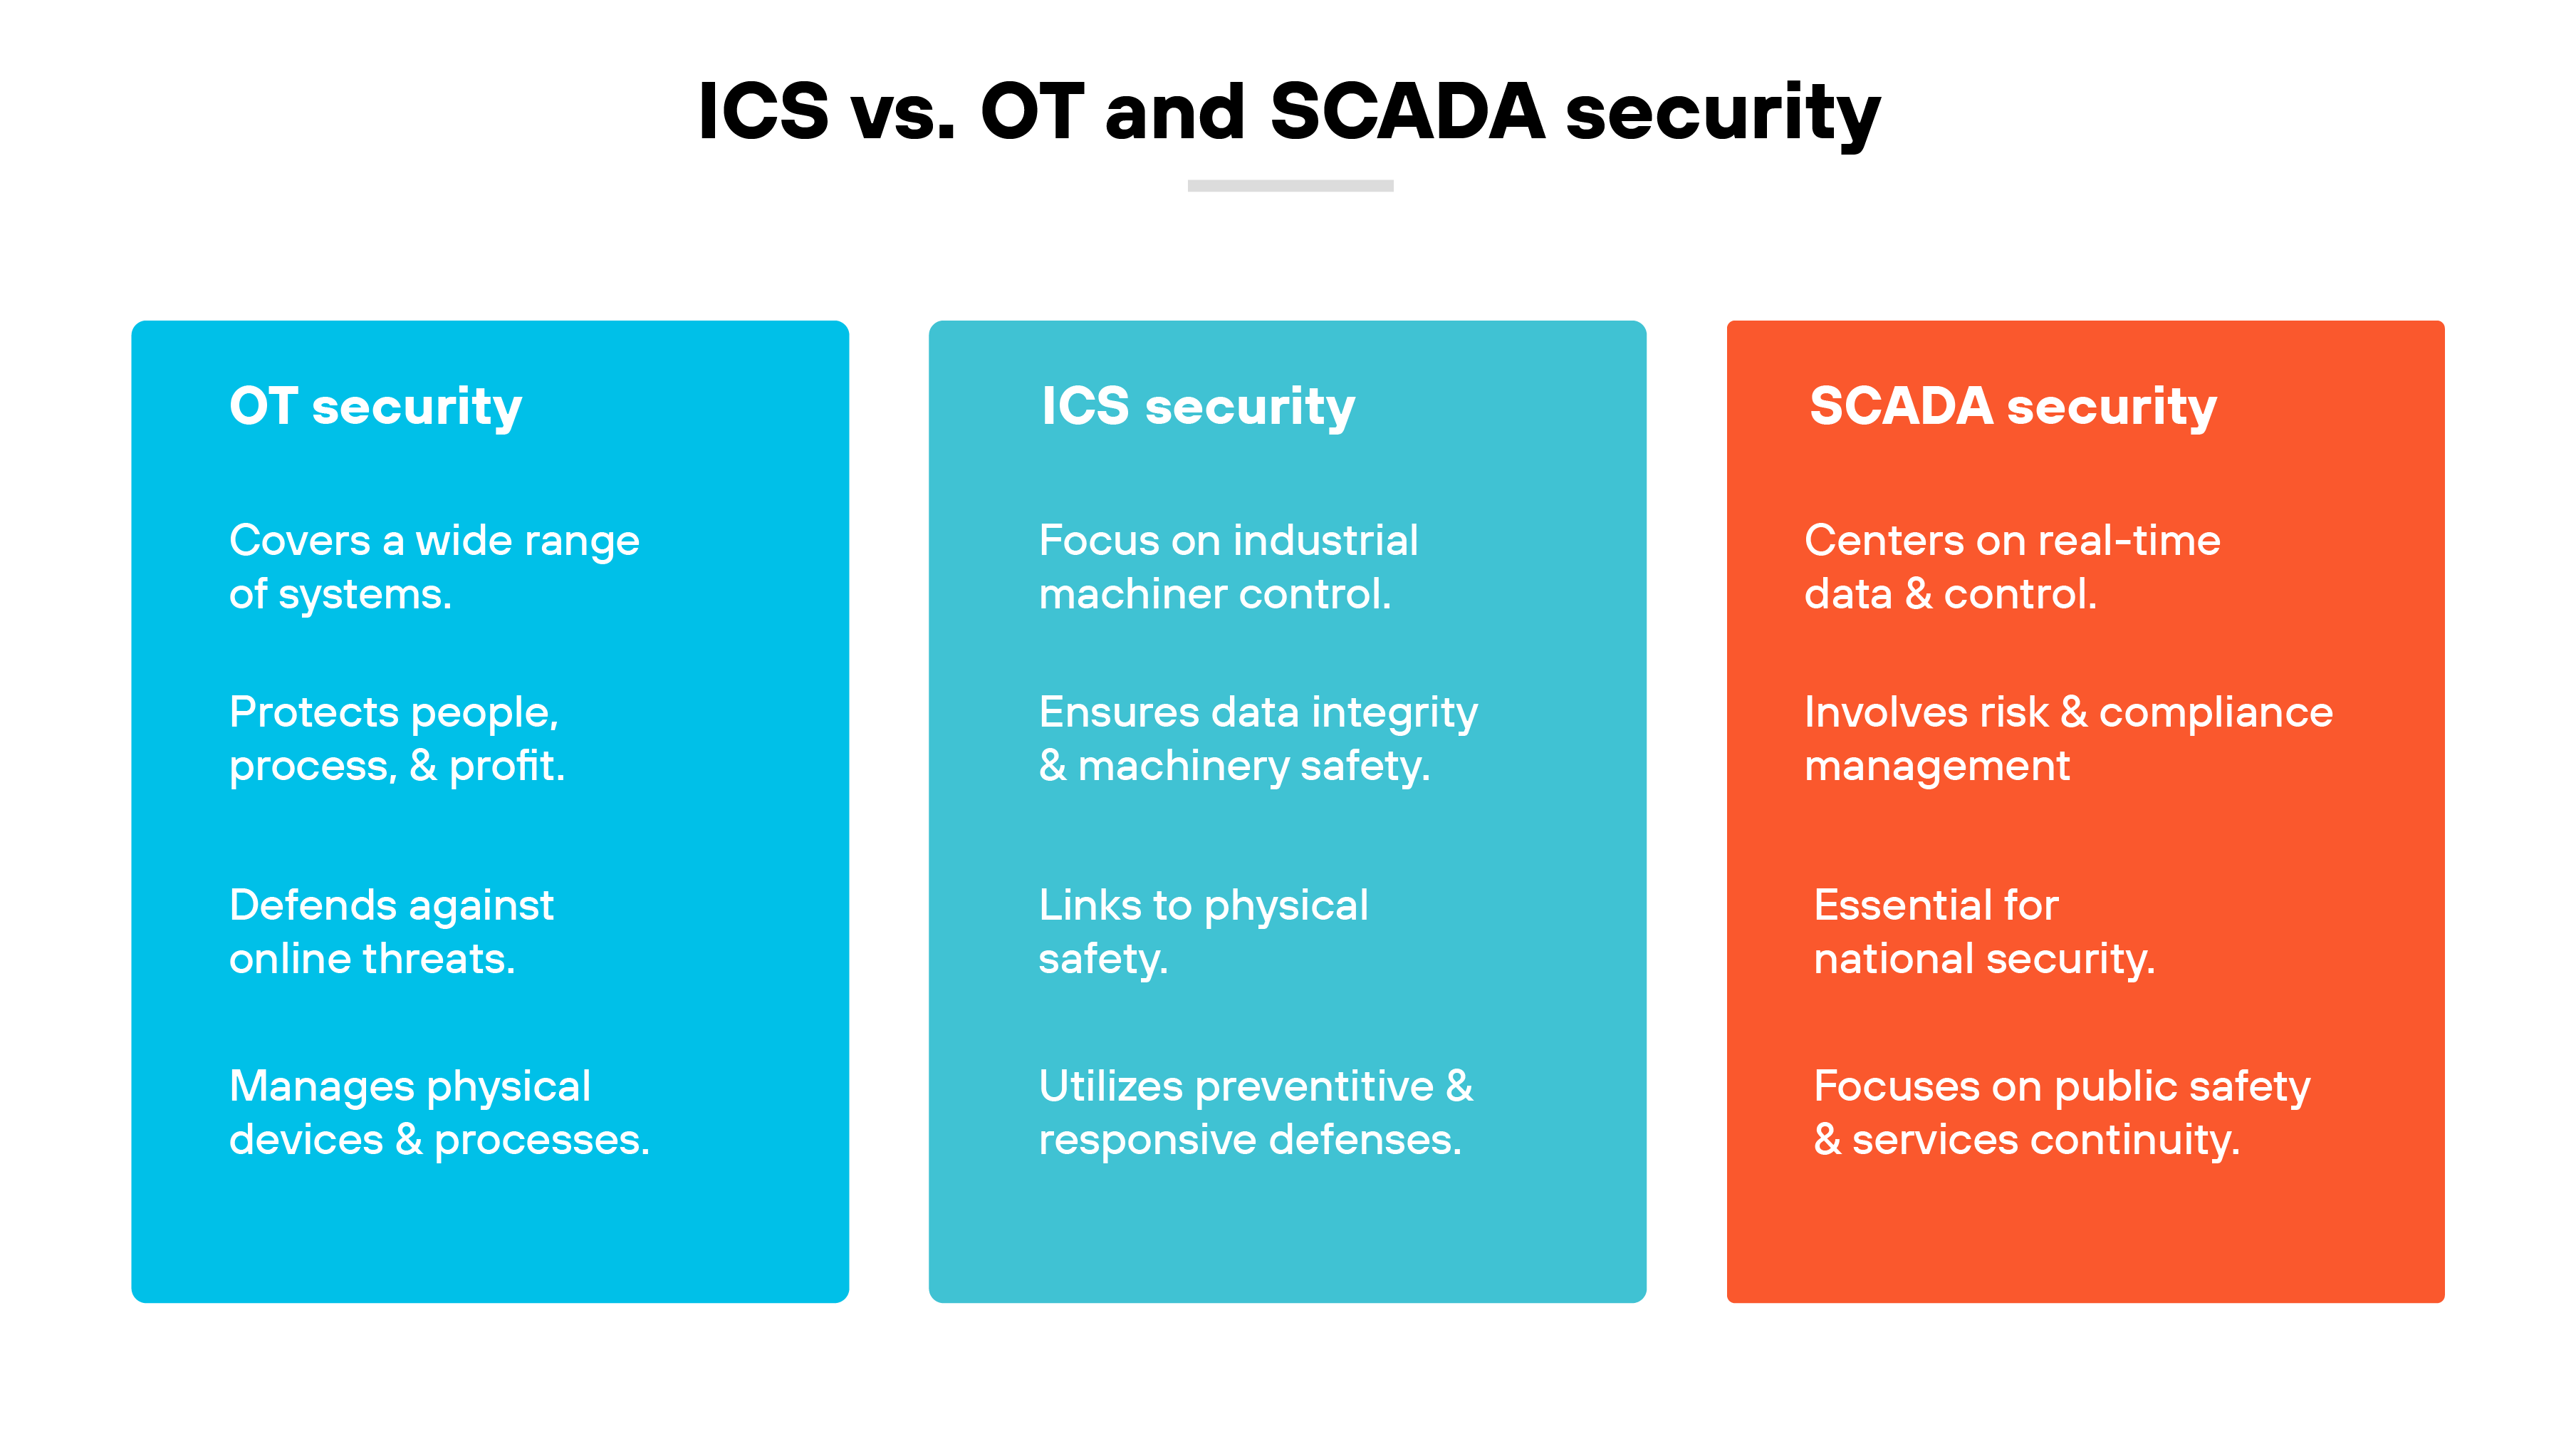
Understanding how industrial technologies overlap helps security architects design targeted defenses for specific operational layers.
Technology Domain
Core Purpose
Scope of Operation
Primary Component Examples
Operational Technology (OT)
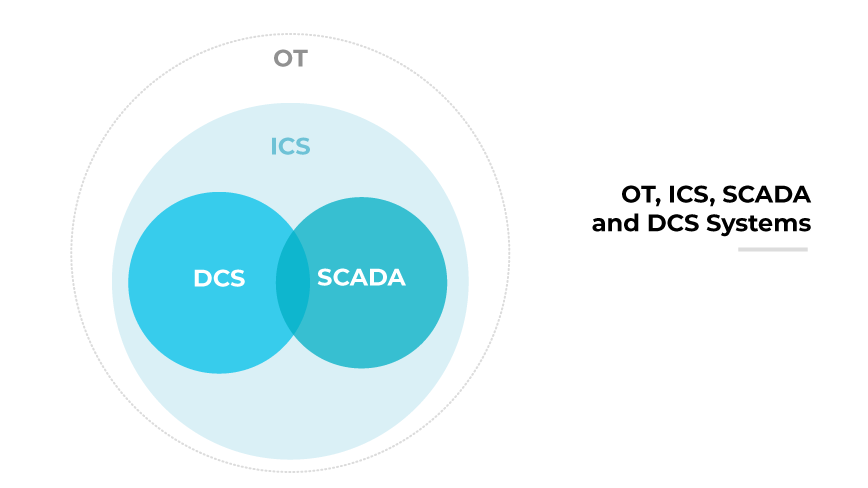
Broad umbrella covering hardware and software that detects or causes changes in physical processes.
Facility-wide physical infrastructure.
Industrial robotics, building automation, environmental controls.
Industrial Control Systems (ICS)
Specific subcategory of OT focused on controlling, automating, and monitoring industrial production.
Plant floor automation and process loops.
PLCs, RTUs, HMIs, control servers, actuators, sensors.
SCADA Systems
Supervisory framework designed for high-level monitoring across vast physical distances.
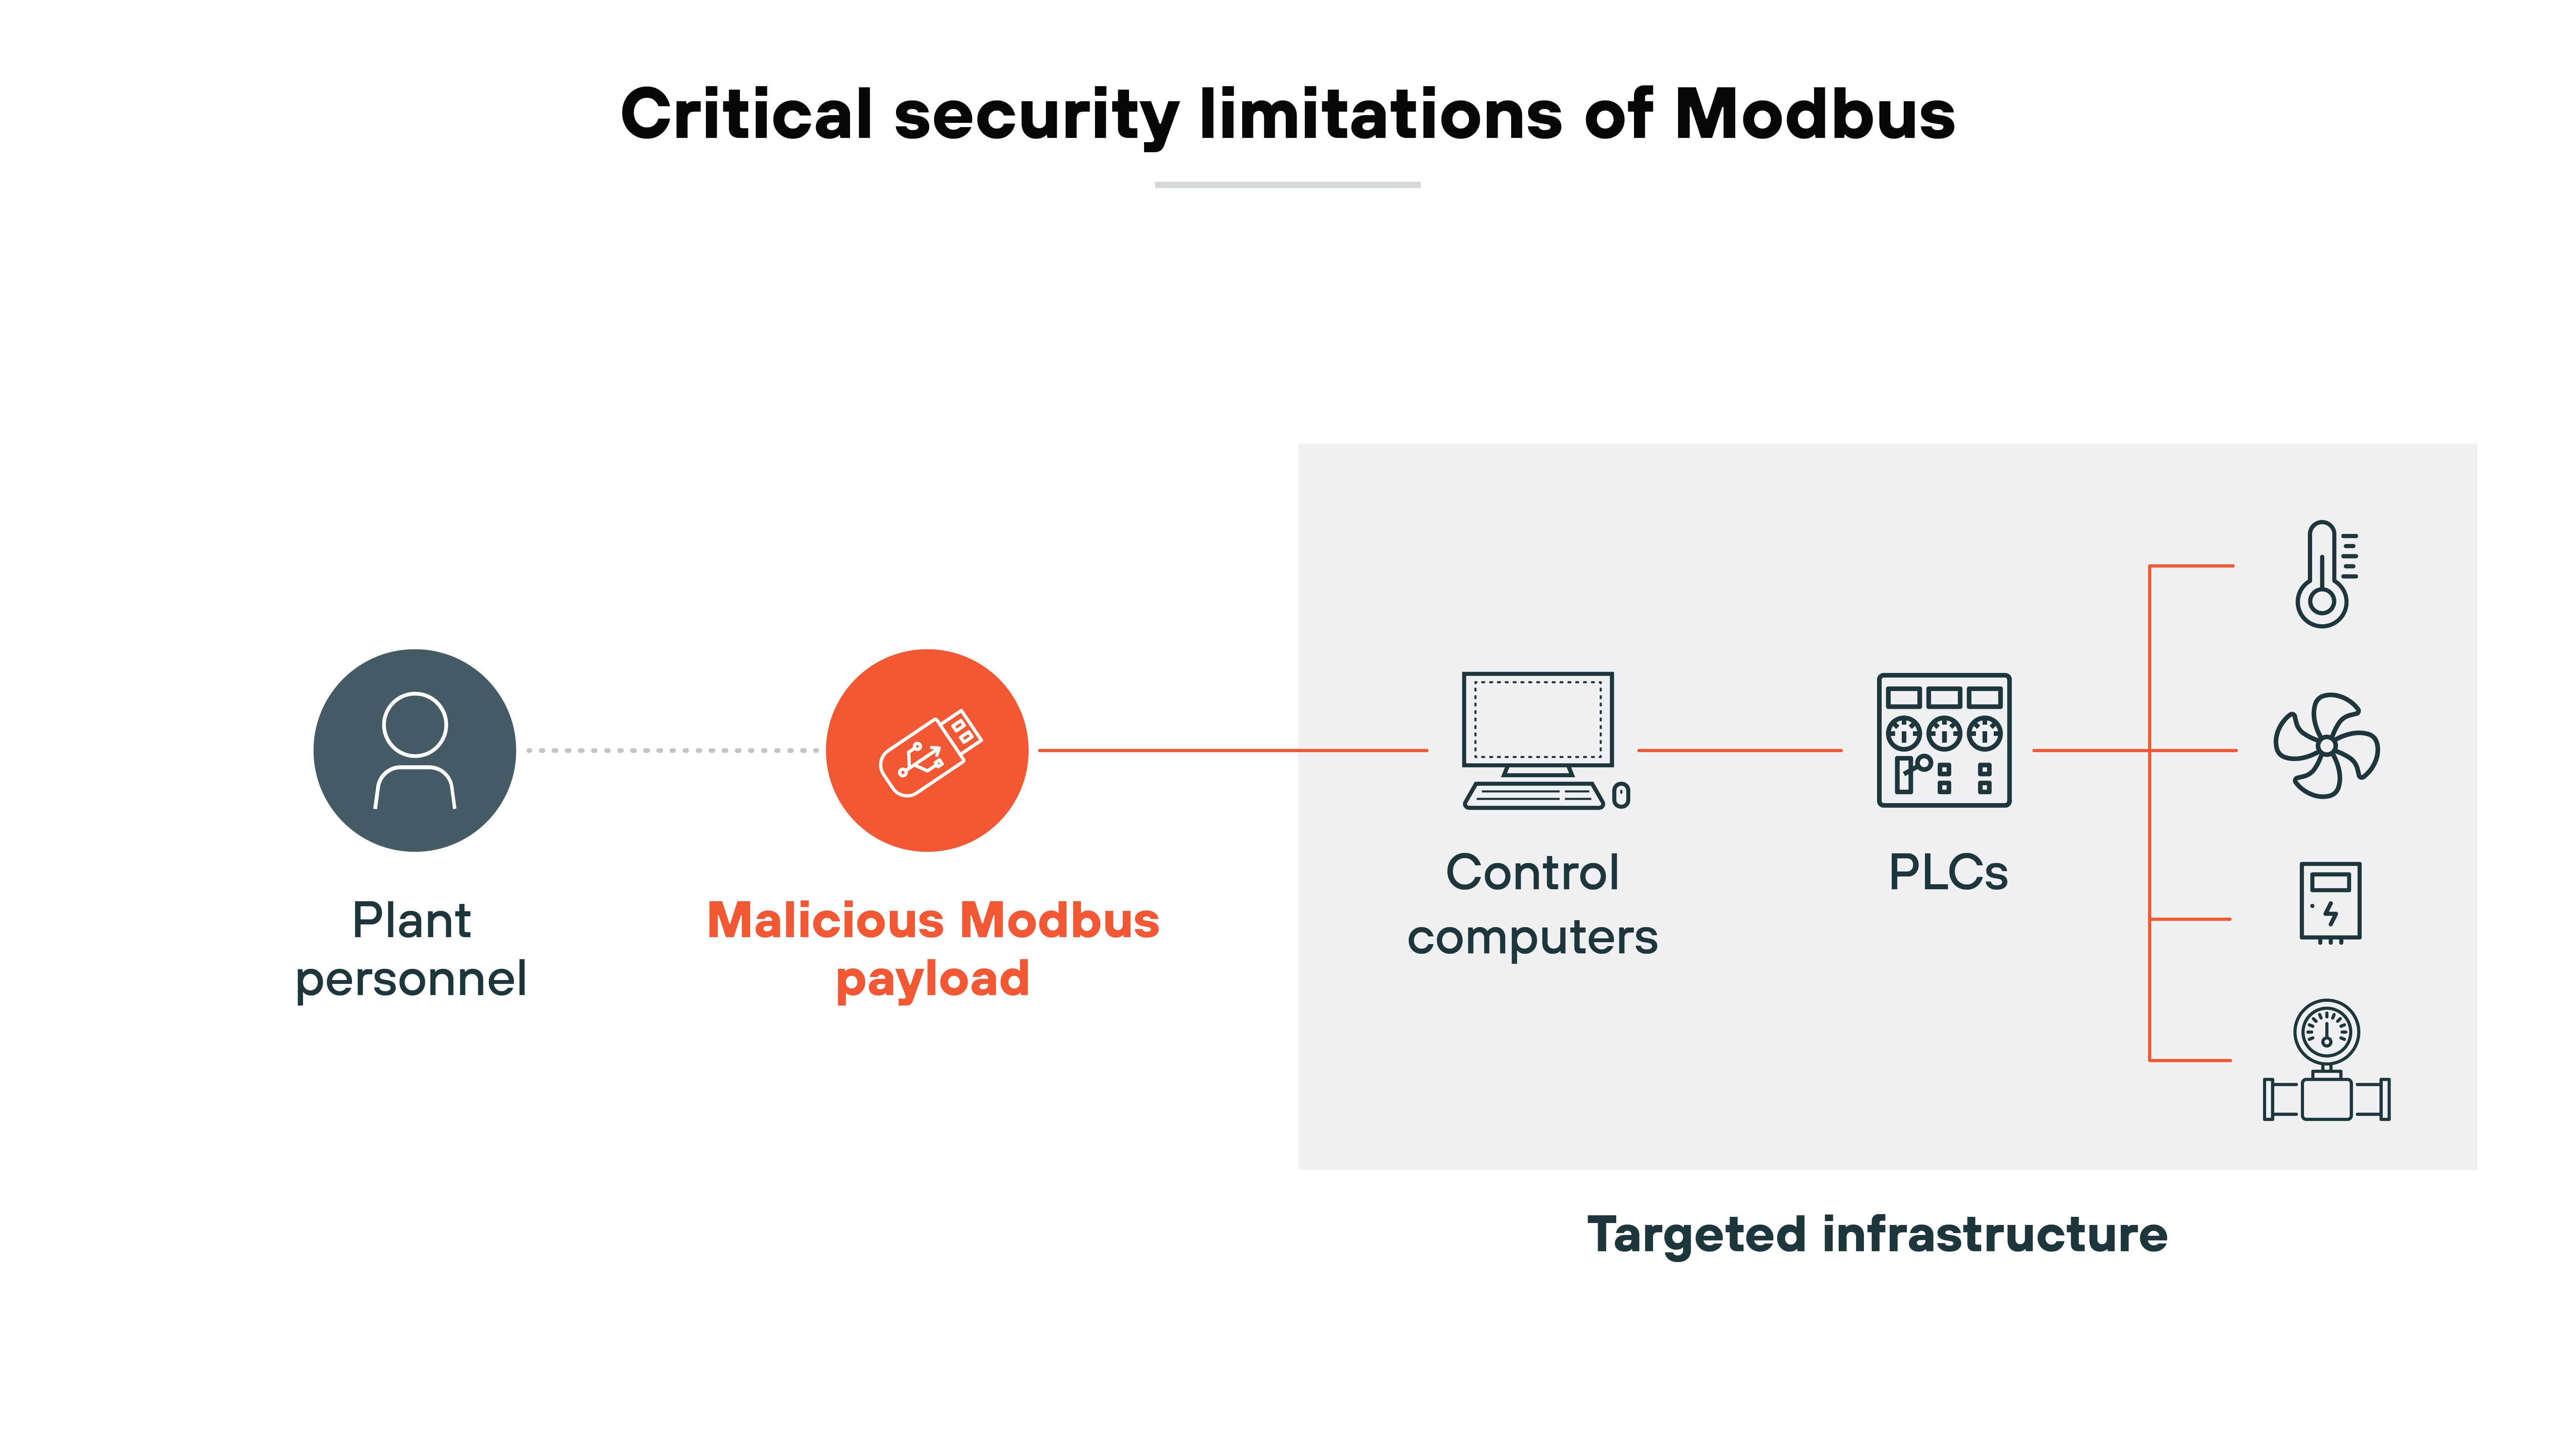
Industrial control system protocols govern communication between field devices, logic controllers, and supervisory systems. Early industrial networks relied on isolated serial connections where security controls were omitted in favor of transmission speed and operational simplicity.
As industrial networks migrated to Ethernet-based architectures, these legacy protocols were encapsulated over standard TCP/IP networks without built-in security controls.
Without modern security controls, industrial protocols are vulnerable to packet sniffing, command injection, and man-in-the-middle attacks. Securing these channels requires network-level access controls, protocol-aware inspection firewalls, and cryptographic protections where supported.
Common ICS Protocol Families
Protocol Family
Primary Operational Role
Native Security Controls
Common Vulnerabilities & Risks
Modbus (RTU / TCP)
Field device communication between PLCs and sensors.
None in standard implementations; TLS optional in Modbus TCP Security.
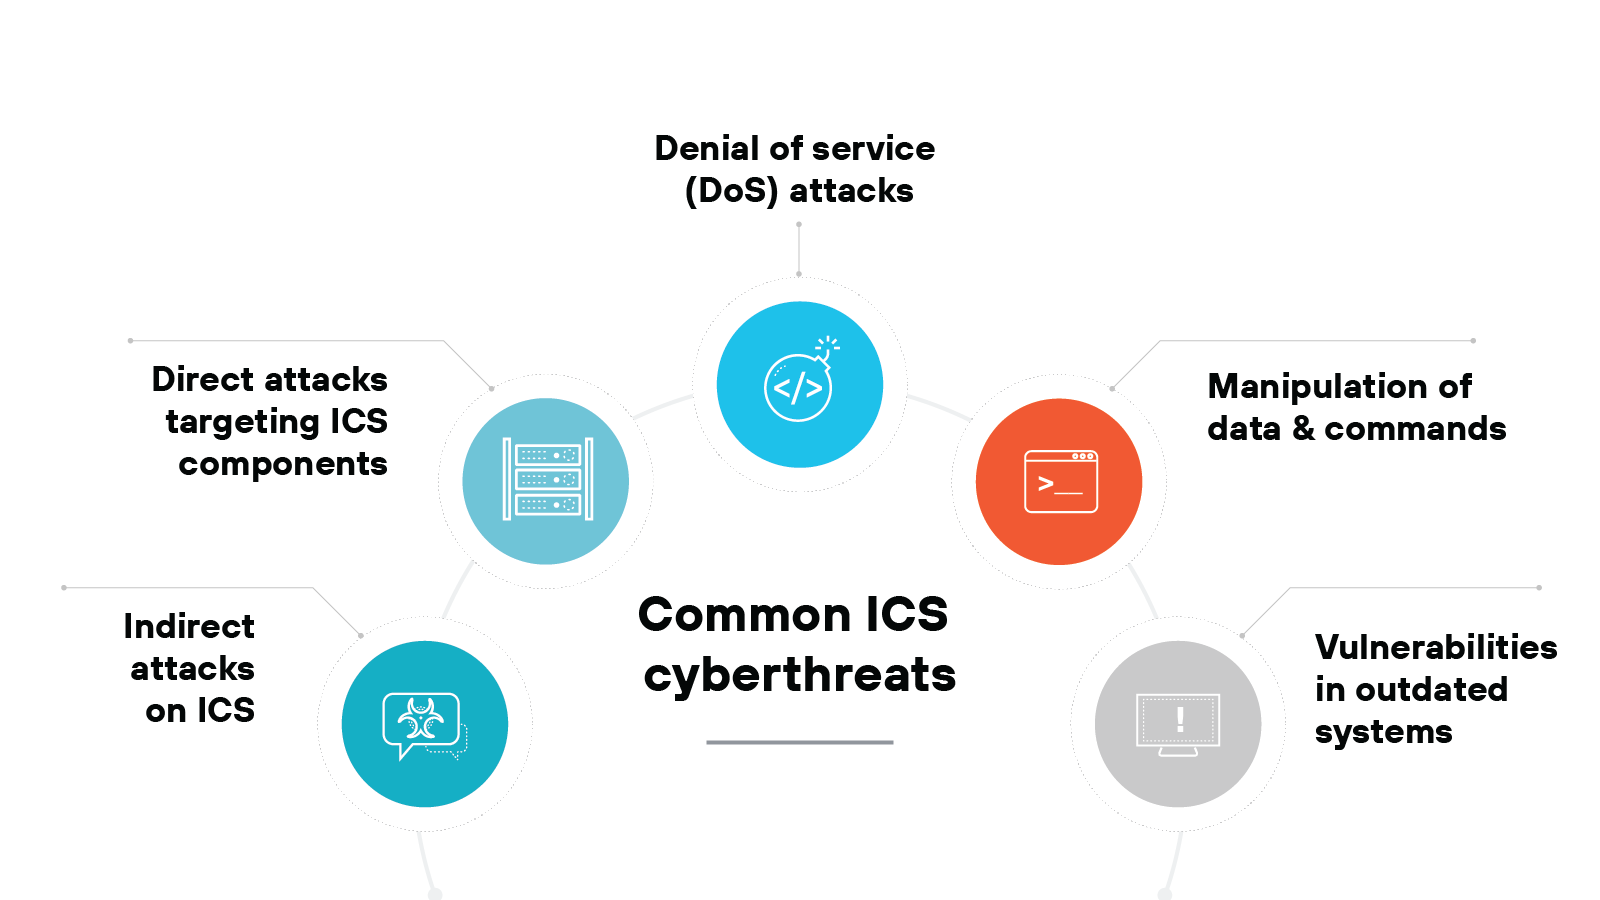
The cybersecurity threat landscape for industrial control systems has expanded rapidly as facilities connect plant floor operations to enterprise networks and internet services. Threat actors actively seek access to industrial networks to steal intellectual property, demand ransom, or sabotage critical physical equipment. Understanding common threat vectors allows defenders to implement targeted countermeasures across both IT and OT environments.
Direct Attacks on ICS Components
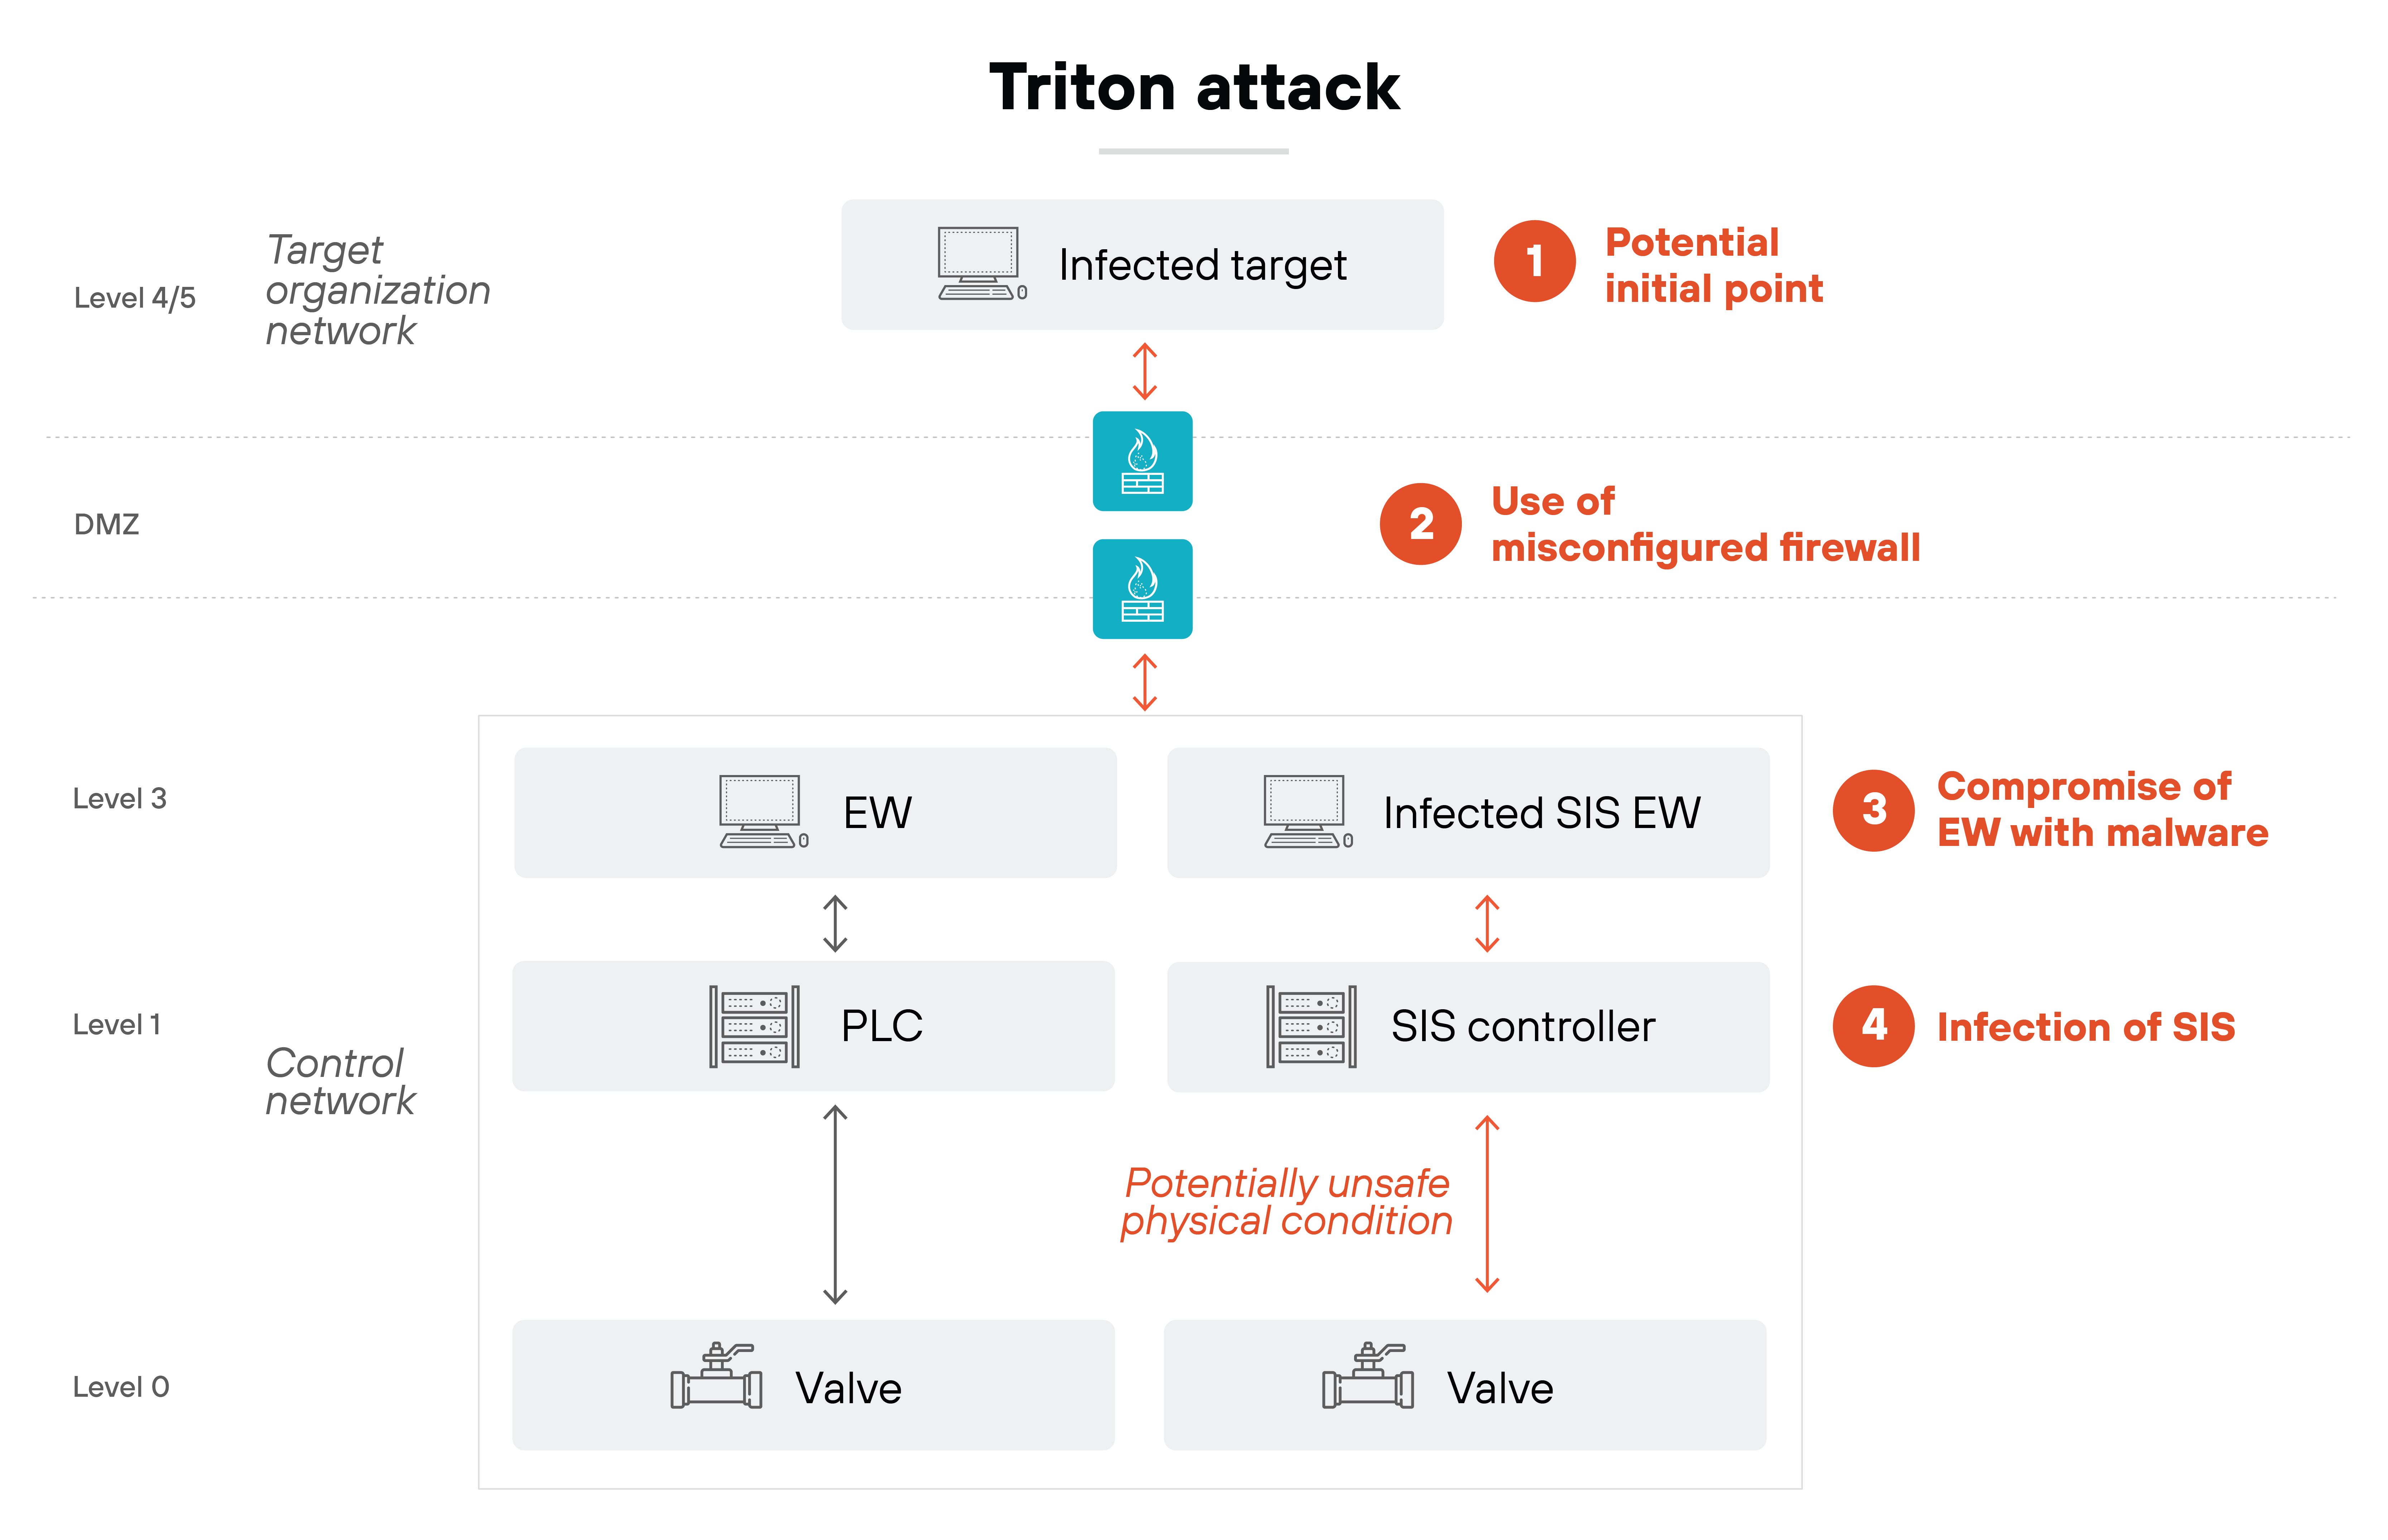
Direct attacks target field-level devices such as programmable logic controllers, remote terminal units, or safety instrumented systems. Attackers attempt to modify device firmware, alter ladder logic, or disable safety mechanisms designed to prevent mechanical disasters.
A prominent example occurred in 2017 when the Triton/Trisis malware targeted Schneider Electric Triconex safety controllers at an industrial facility. The malware attempted to manipulate safety instrumented systems, demonstrating that threat actors actively target physical safety mechanisms to cause operational disruptions.
Indirect Attacks via IT/OT Convergence
Indirect attacks originate within traditional enterprise IT environments before pivoting into connected industrial control networks. Attackers breach corporate email systems or business databases, compromise shared network credentials, and traverse corporate firewalls into control zones.
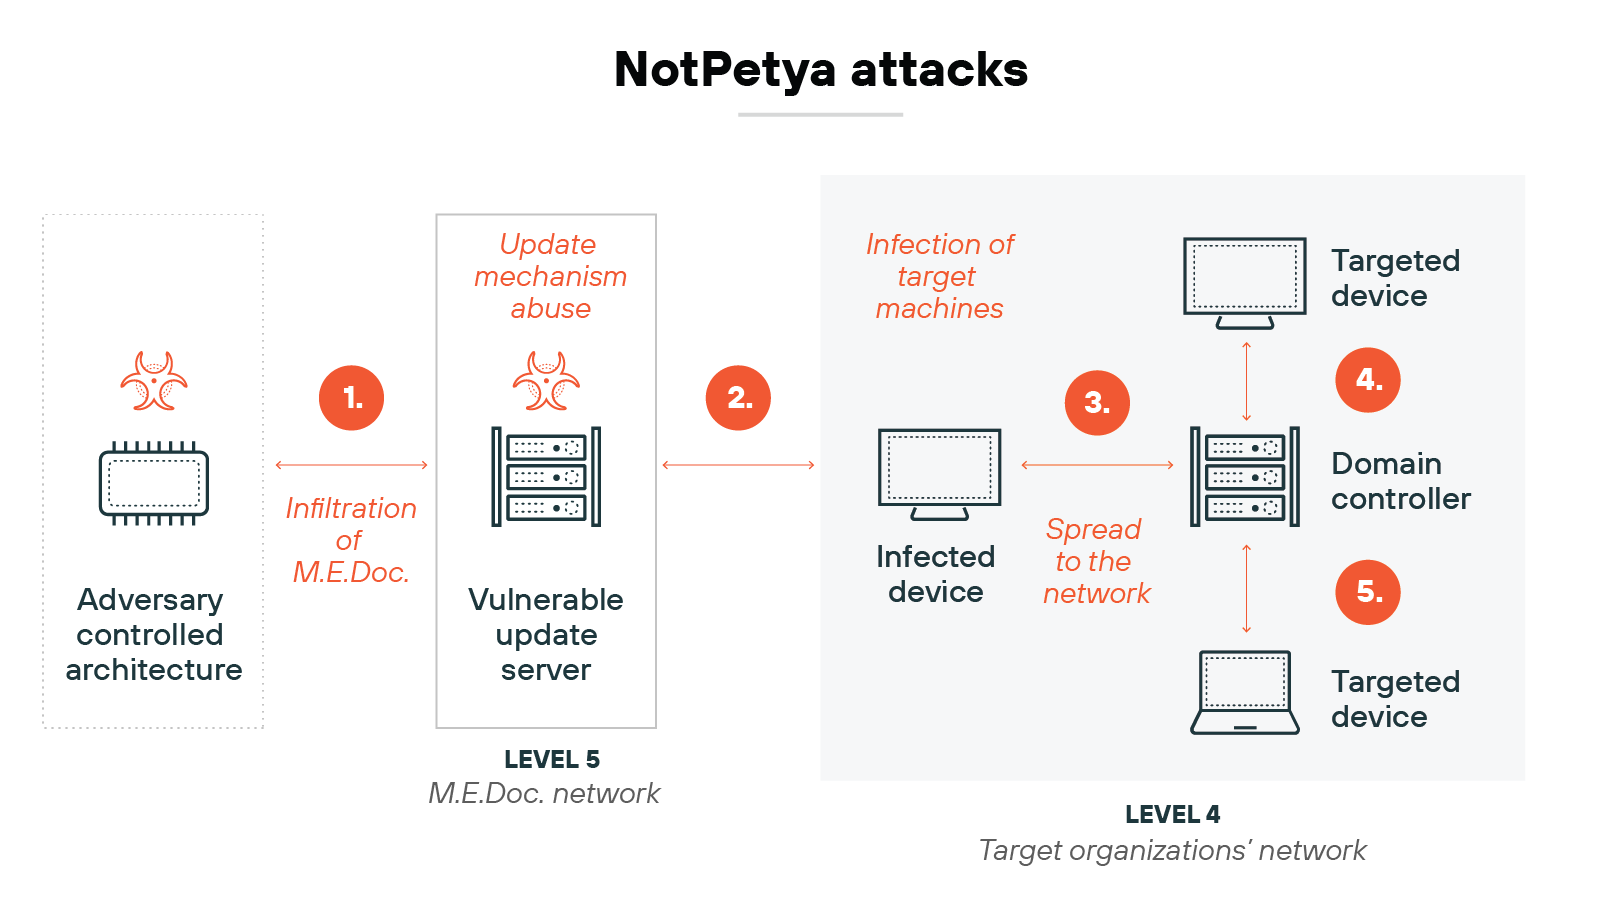
The 2017 NotPetya malware outbreak illustrated this risk when ransomware infected corporate IT infrastructure before spreading rapidly across global supply chains and operational facilities. Automated propagation features forced major logistics, energy, and manufacturing organizations to shut down physical production lines.
Data manipulation attacks involve intercepting operational traffic and injecting false measurement values or unauthorized control commands into the network. Attackers alter sensor readings displayed on operator consoles, misleading human operators into taking unsafe corrective actions.
In 2016, the Industroyer malware directly manipulated industrial network protocols to send unauthorized control commands to electrical substation switches in Ukraine. The attack bypassed supervisory safeguards and caused widespread electrical power outages.
Denial of Service and Legacy Vulnerabilities
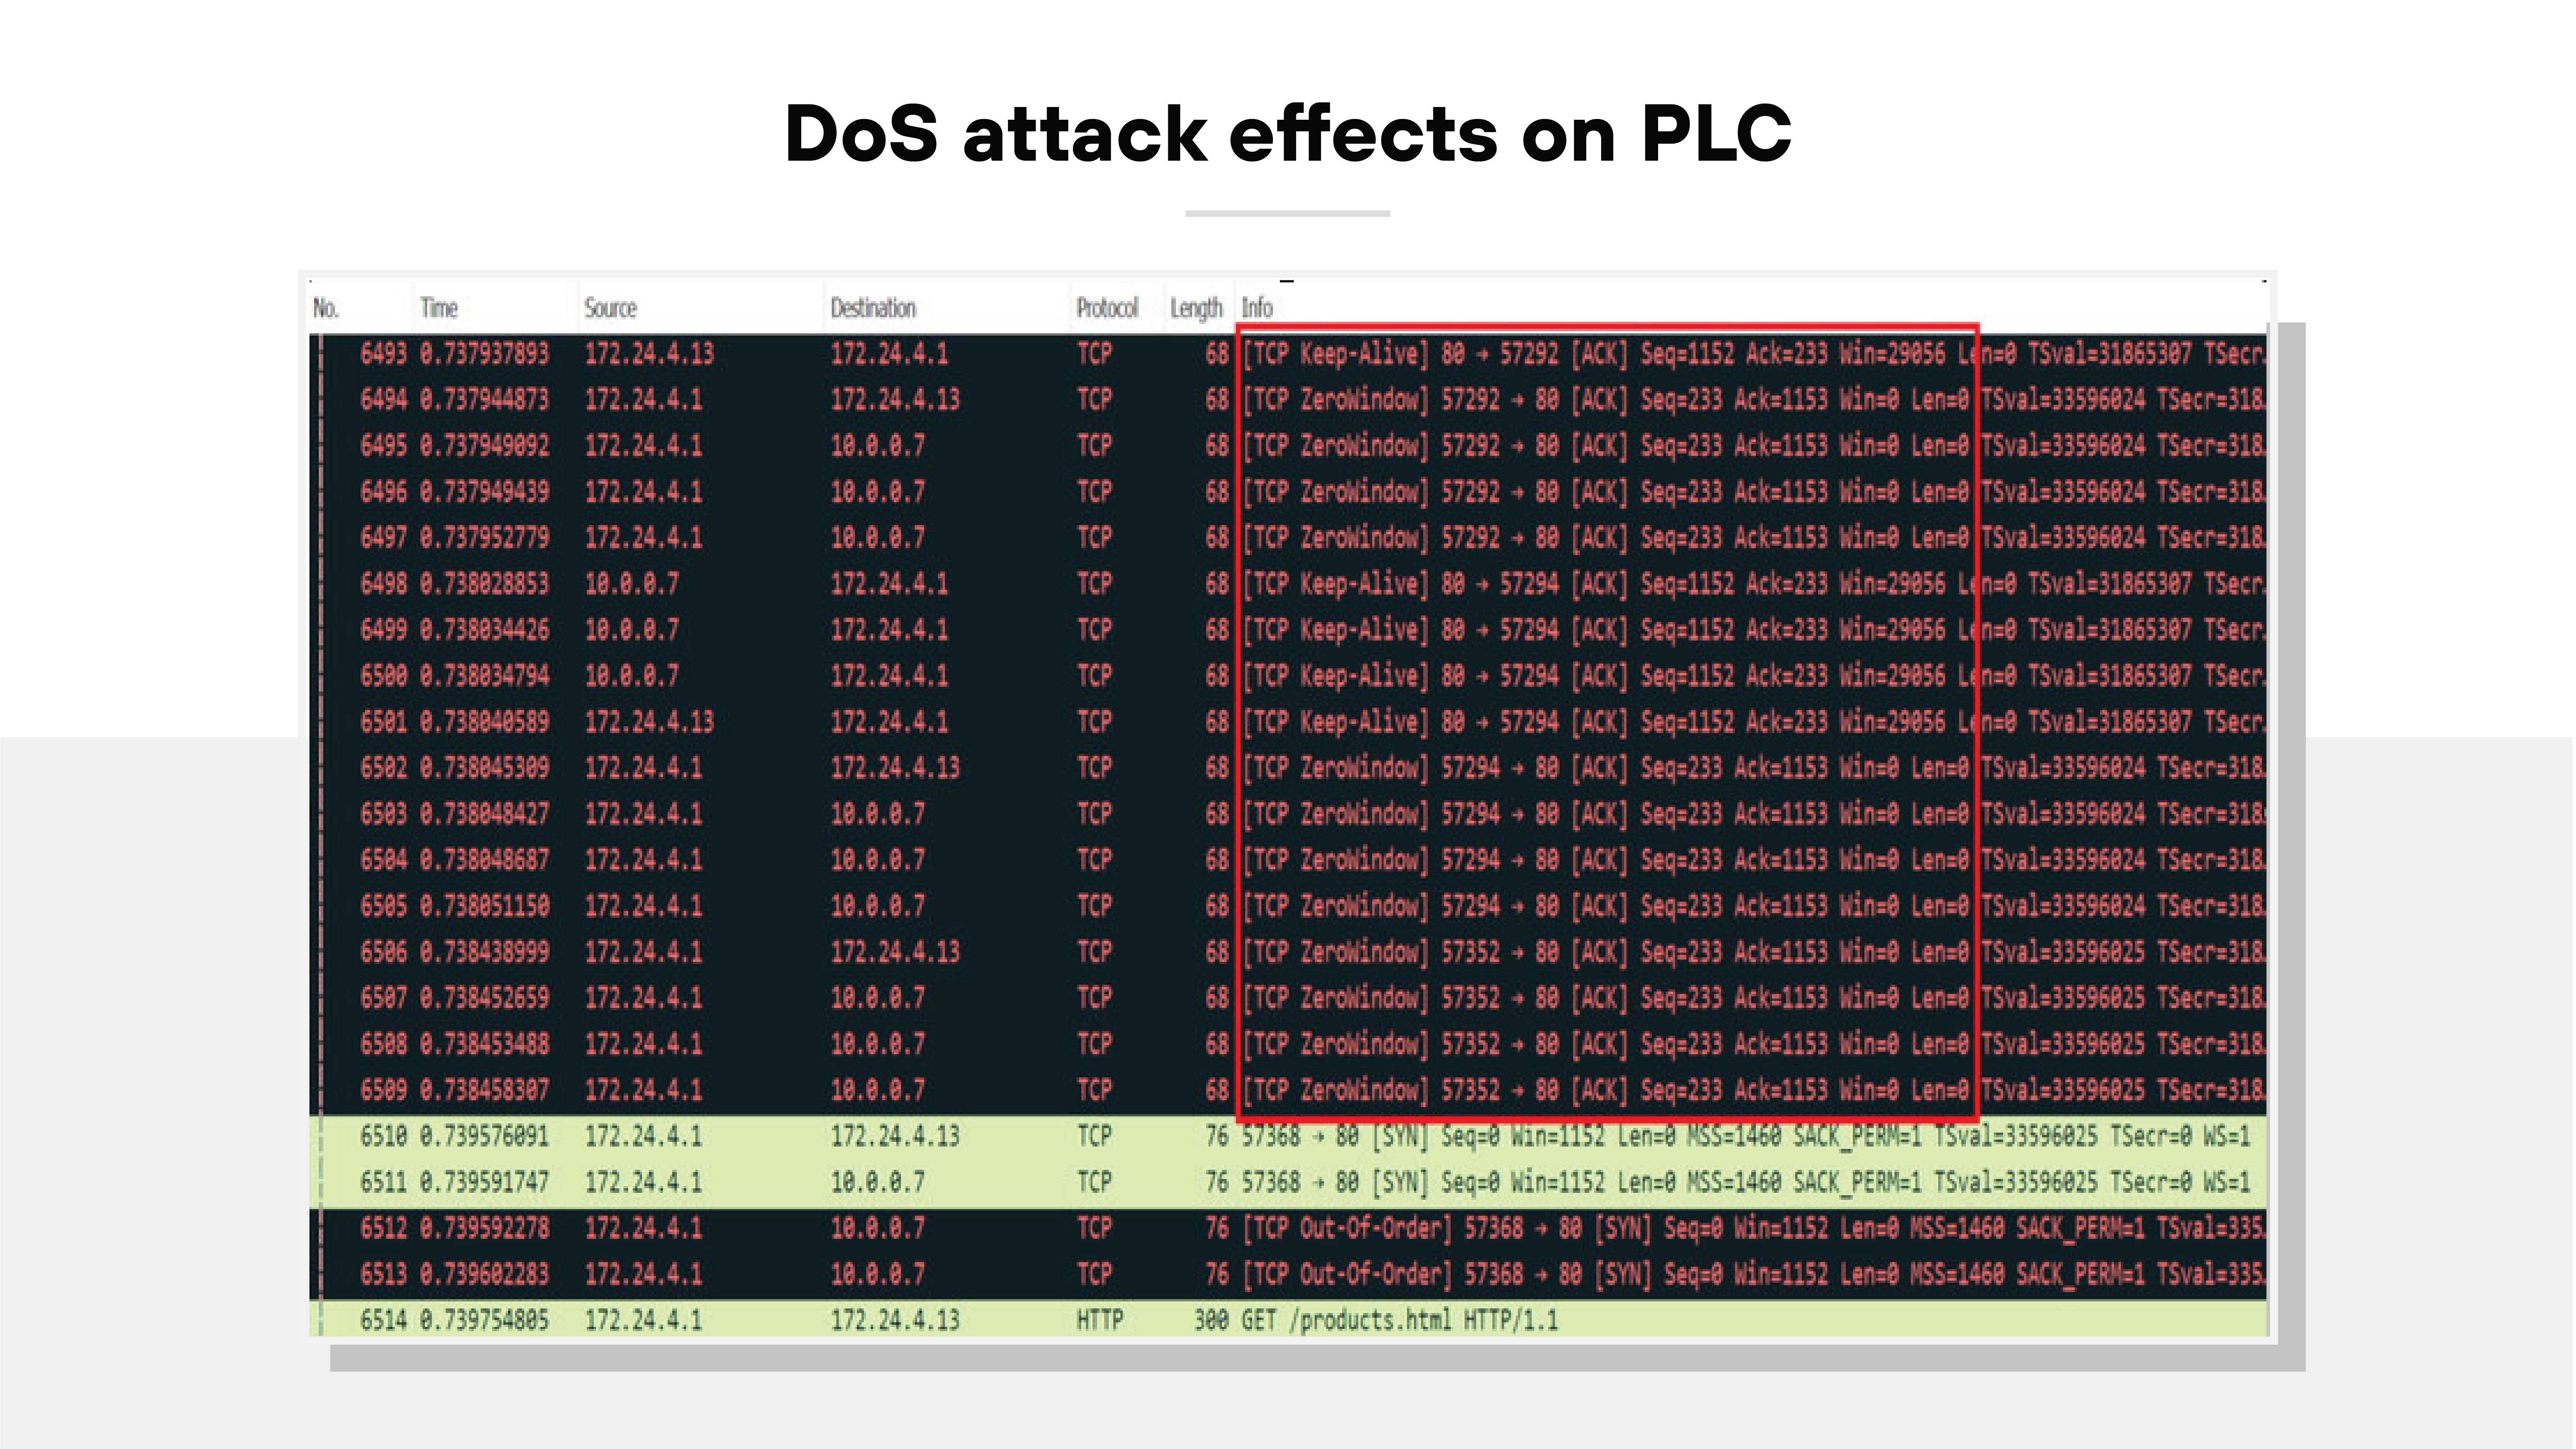
Denial of service attacks flood industrial networks or field controllers with excessive traffic, overwhelming processing capabilities and delaying critical process commands. Because legacy controllers feature limited processing power, even basic network scanning traffic can cause unpatched devices to crash.
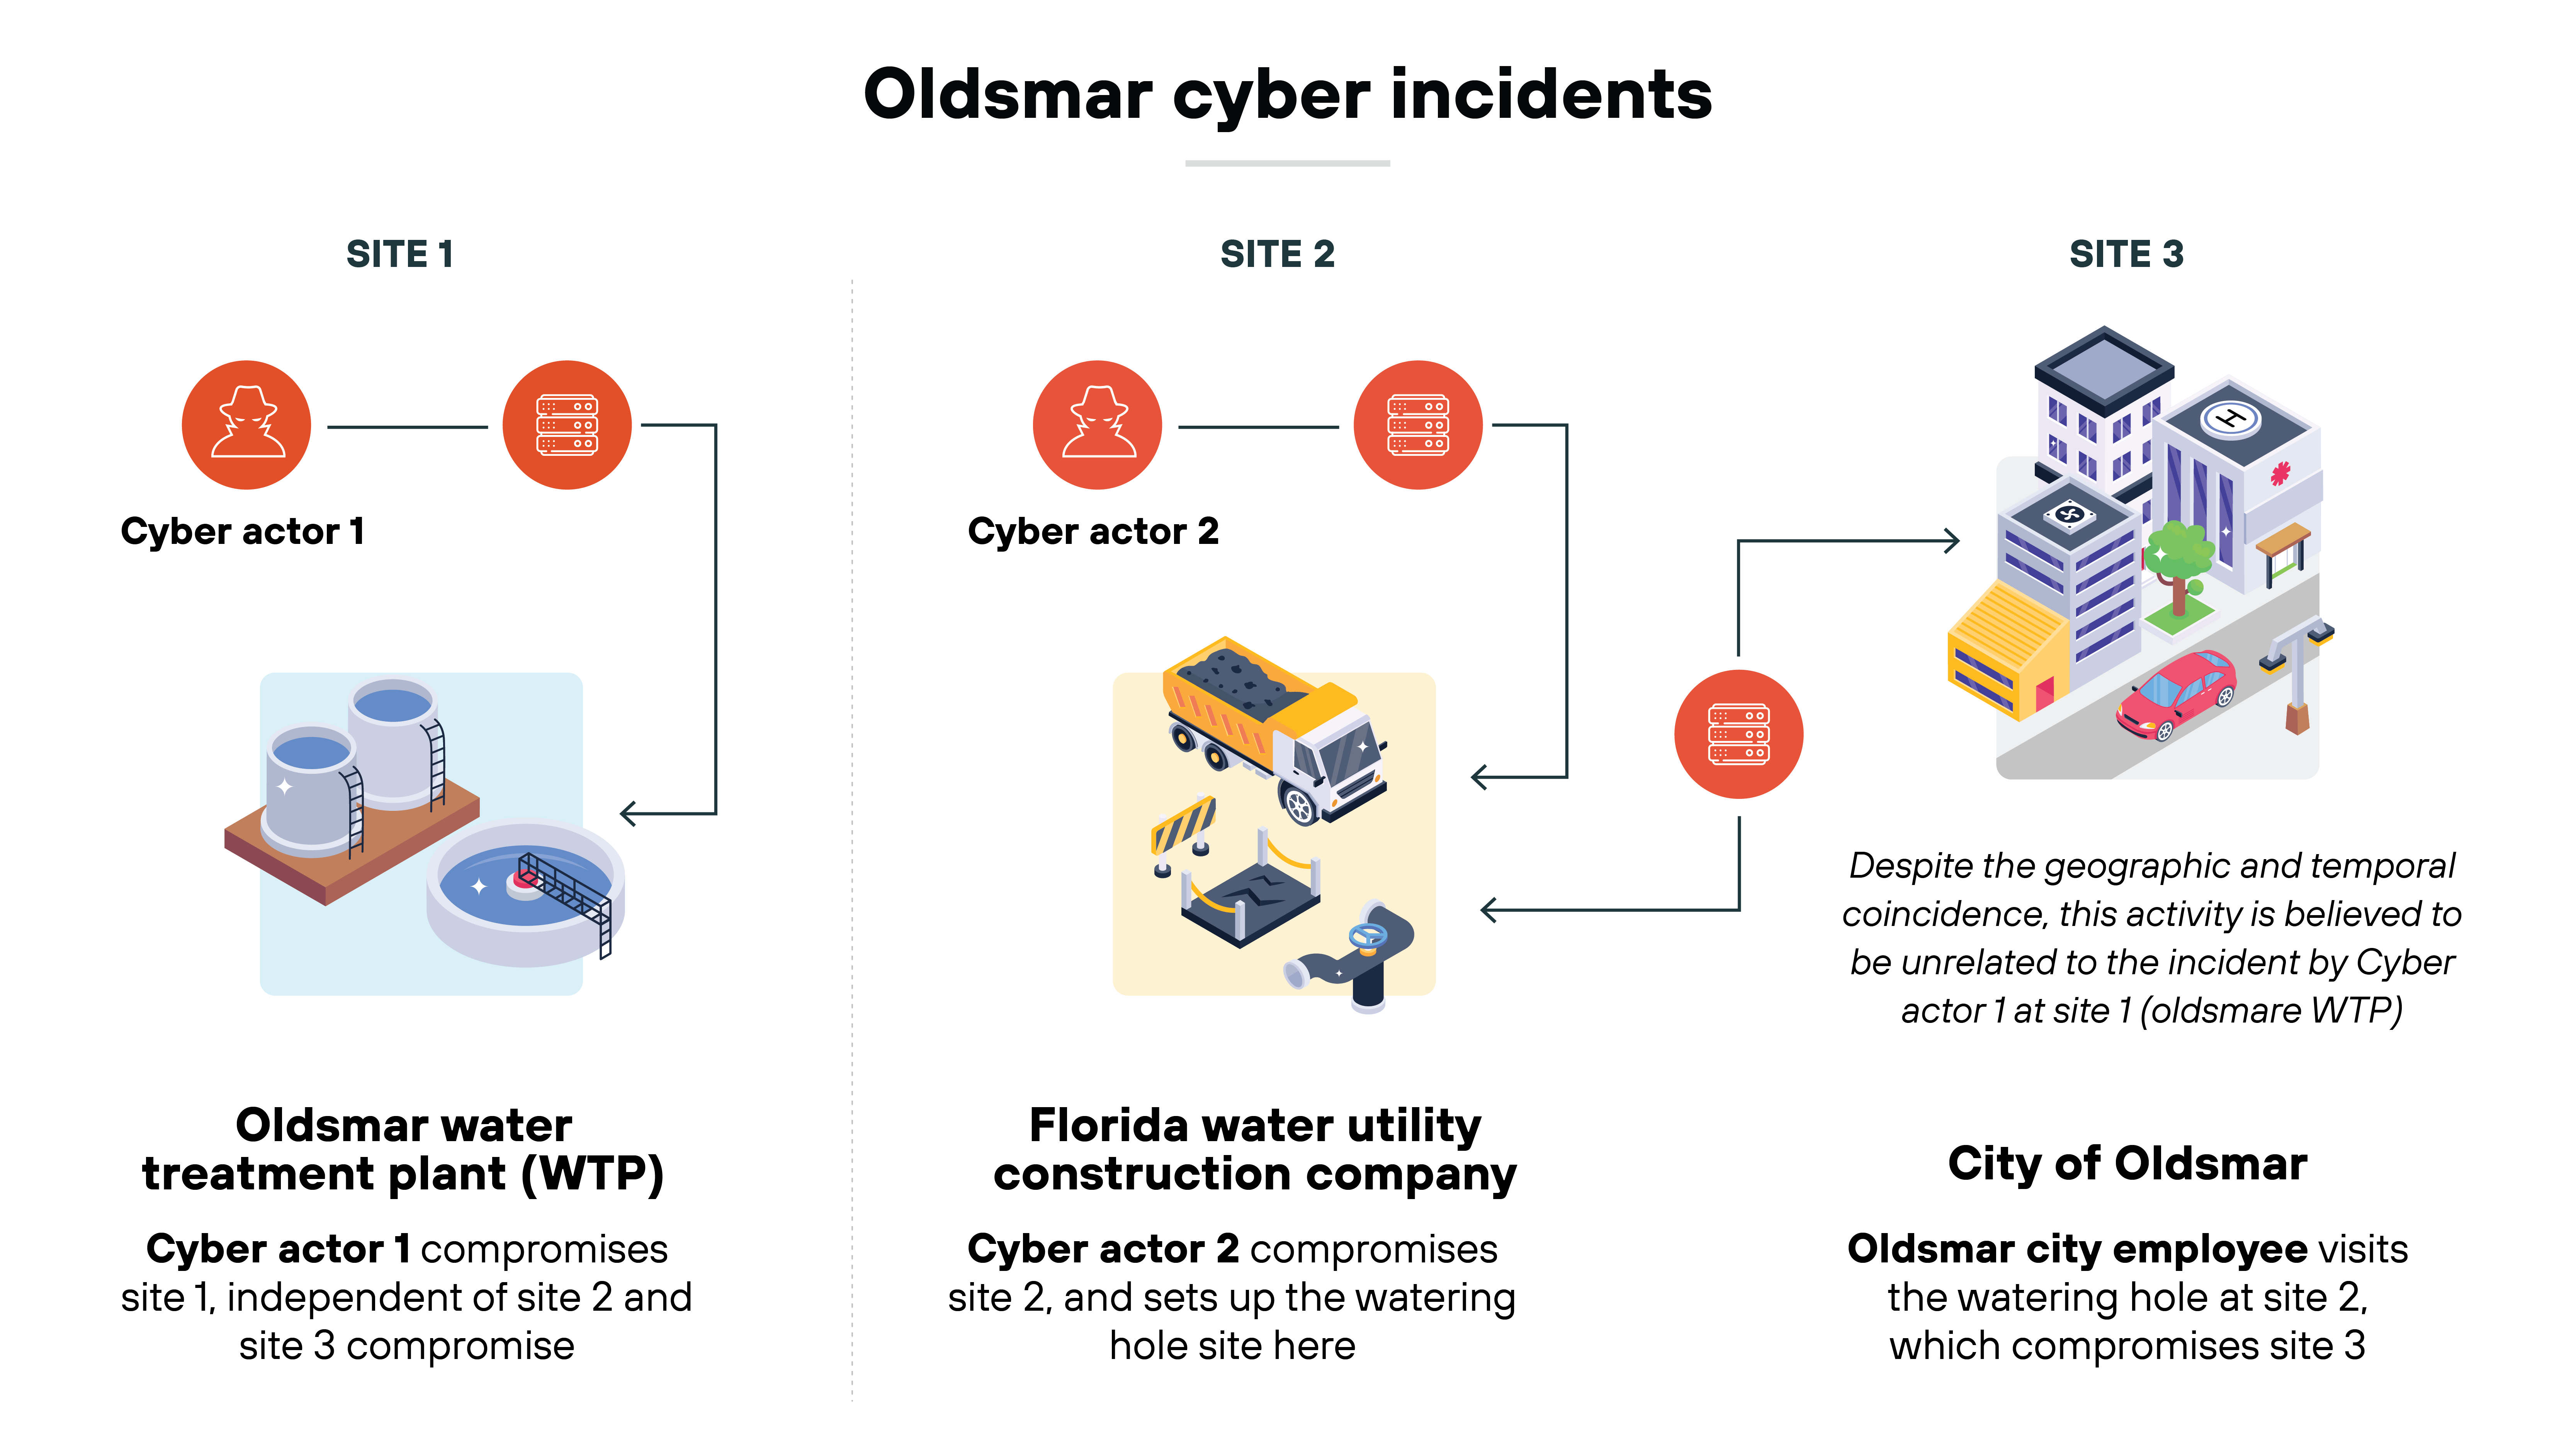
In 2021, an unauthorized user accessed an outdated remote management platform at the Oldsmar, Florida water treatment plant. The attacker attempted to increase sodium hydroxide concentrations to dangerous levels before an operator manually intervened, underscoring the risks of legacy remote access tools.
Major ICS Security Challenges
Securing industrial control systems involves managing unique operational constraints that do not exist in conventional IT environments. Security teams must protect vital machinery while honoring strict process requirements and physical safety mandates.
Real-Time Performance Demands and Zero Downtime Mandates
Industrial processes operate under microsecond execution requirements where network latency or packet loss can trigger system trips. Security measures such as automated antivirus scanning, deep packet decryption, or intrusive network discovery can degrade process performance. Furthermore, scheduled system reboots for software updates are rarely feasible in facilities designed for continuous multi-year operation.
Legacy Infrastructure and Patch Management Constraints
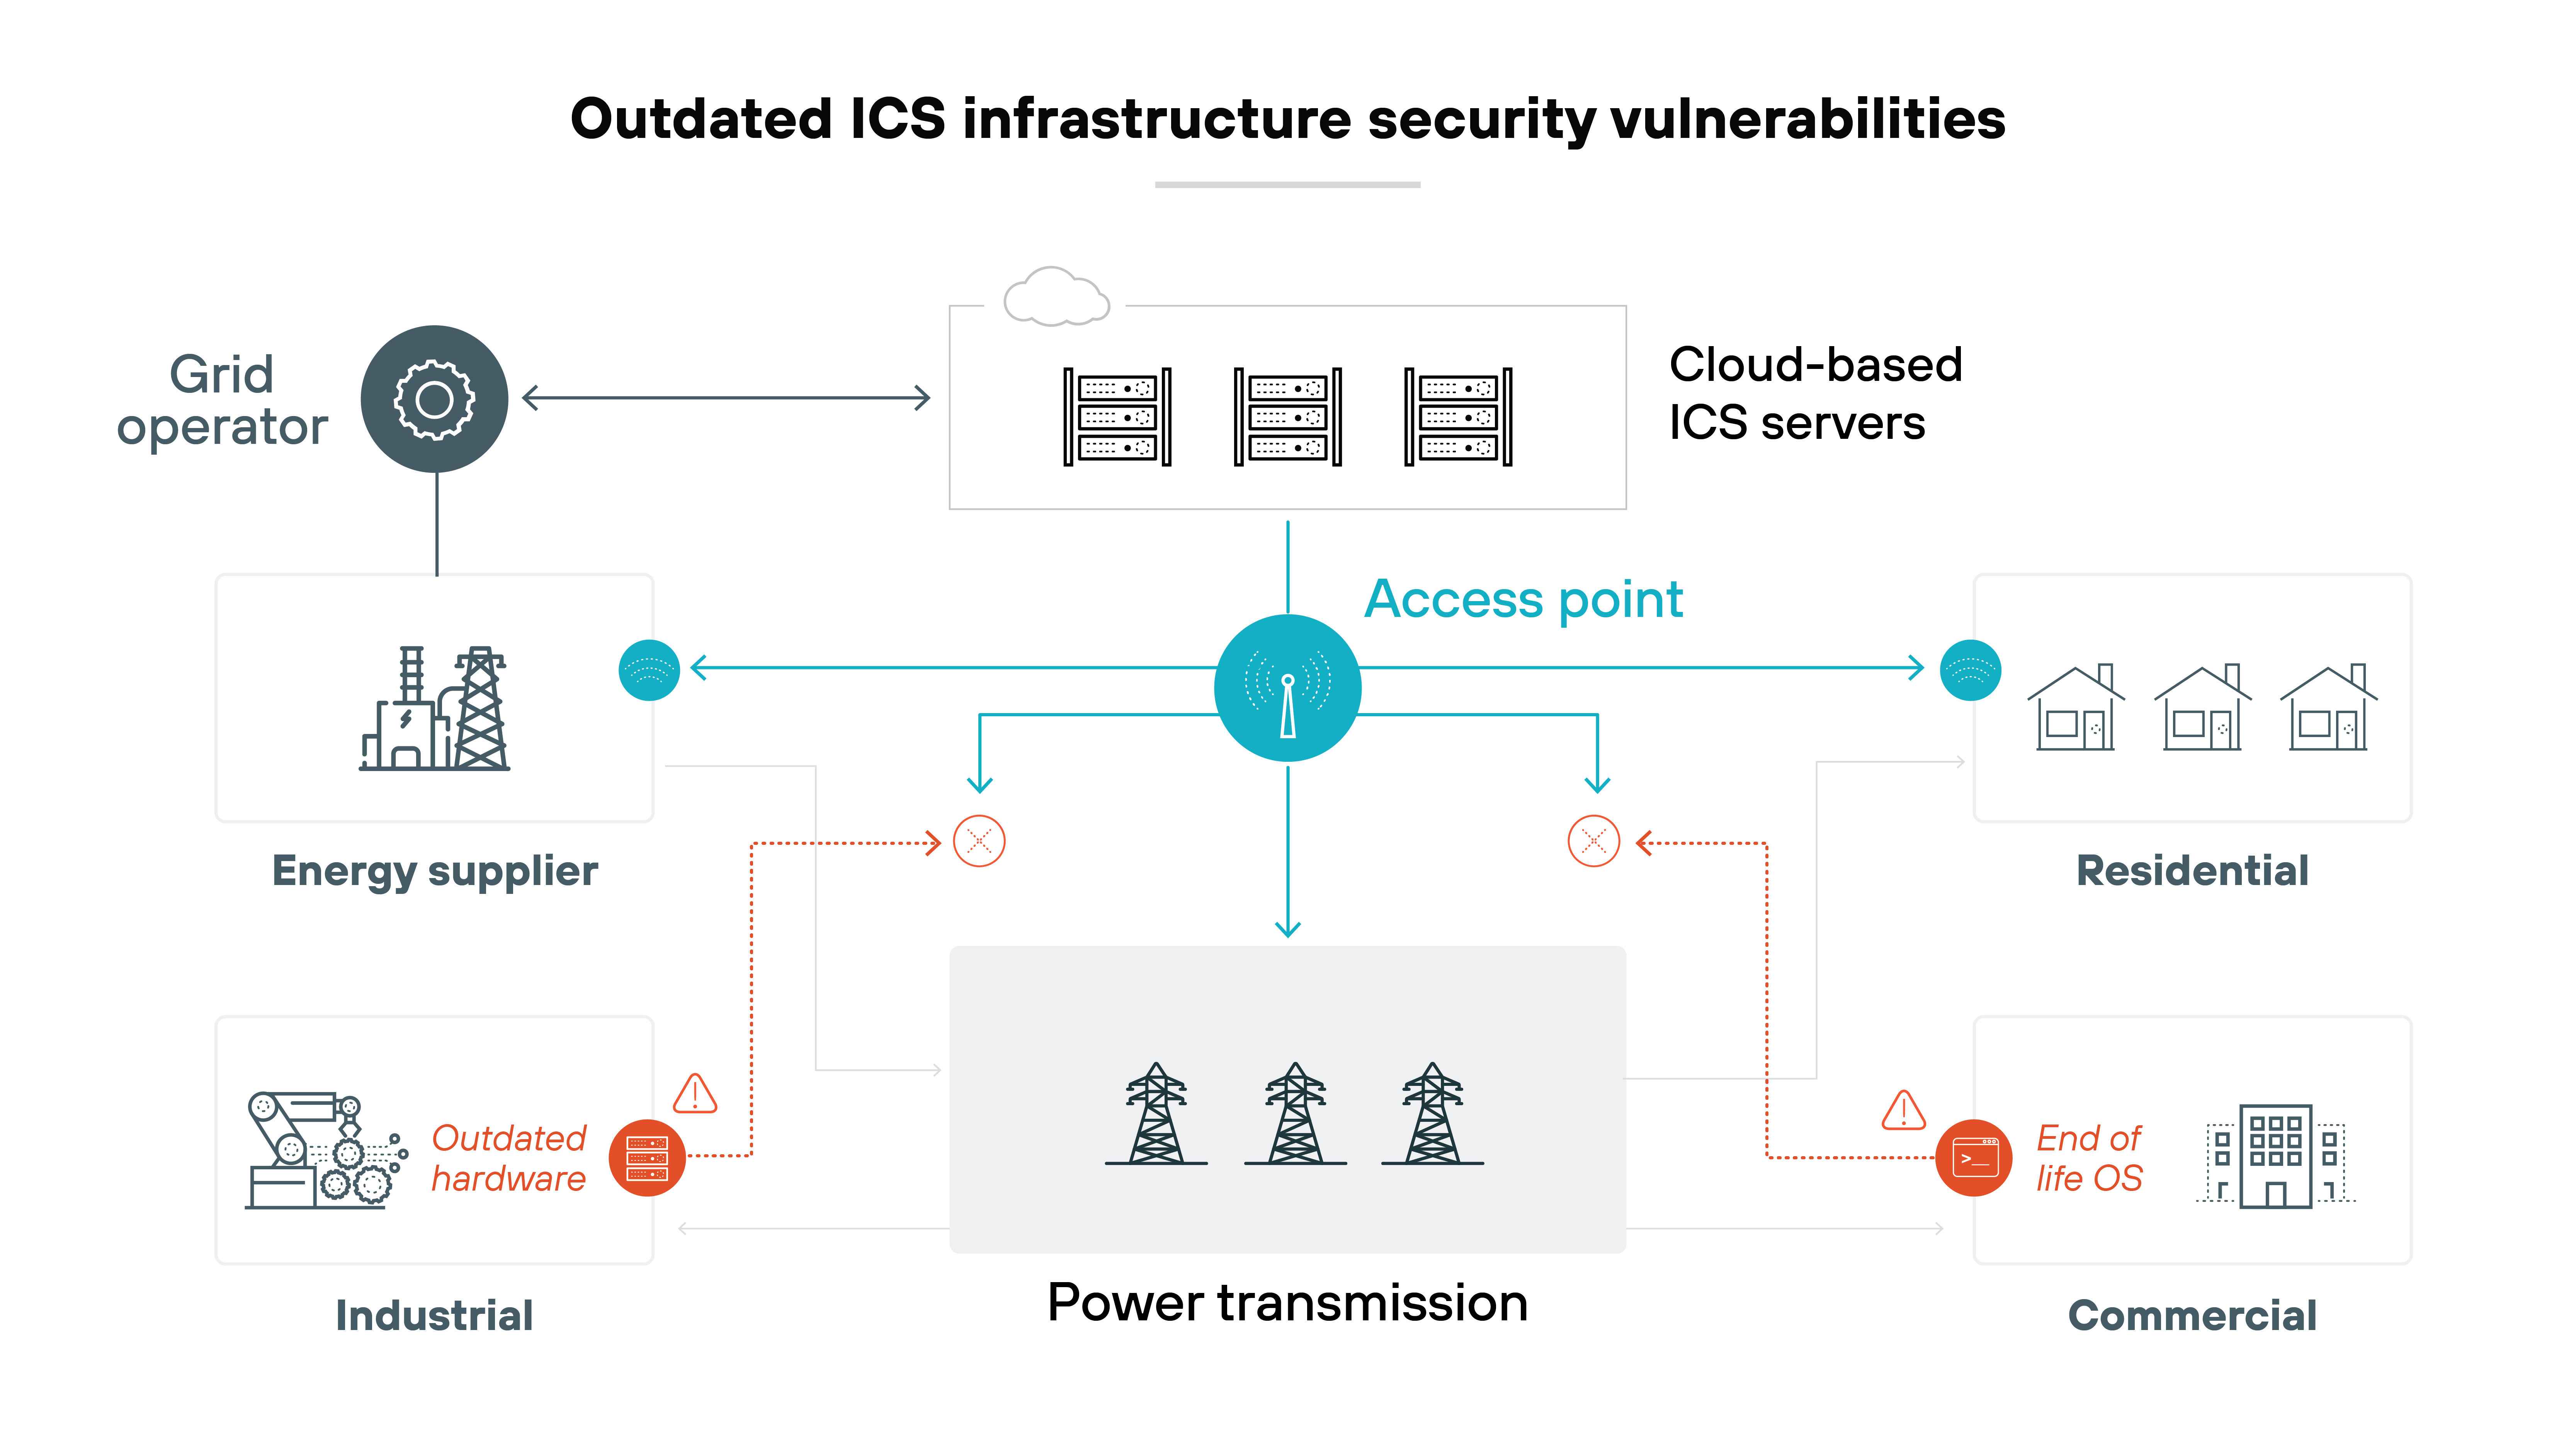
Many industrial environments rely on hardware and software deployed decades ago, long before modern cybersecurity threats emerged. Legacy logic controllers often lack support for strong passwords, user authentication, or encrypted communication.
Effective vulnerability management is particularly challenging because applying software patches requires rigorous laboratory testing and scheduled maintenance shutdowns, leaving legacy vulnerabilities exposed for extended periods.
Cybersecurity Skills Gap in OT Operations
A cultural and technical divide often persists between traditional IT cybersecurity teams and industrial engineering personnel. IT security professionals understand threat mitigation, access controls, and network monitoring, but may lack familiarity with industrial engineering processes. Conversely, plant engineers excel at physical safety and process optimization, but may lack formal training in cyber risk management.
Core ICS Security Frameworks, Standards, and Regulations
Industrial security frameworks provide structured guidance for assessing operational risks, building secure architectures, and demonstrating regulatory compliance. Adopting recognized standards helps organizations establish repeatable security controls across distributed engineering environments.
Standard / Framework
Governing Body
Primary Focus & Guidance
ISA/IEC 62443
International Society of Automation / IEC
Comprehensive framework defining technical requirements, security zones, conduits, and product development lifecycles for industrial automation.
NIST SP 800-82 (Rev. 3)
National Institute of Standards and Technology
Specific guidance for securing operational technology, including SCADA, DCS, and PLC environments, within risk management frameworks.
NERC CIP
North American Electric Reliability Corporation
Mandatory cybersecurity standards regulating the bulk power system, focusing on electronic perimeters, asset management, and incident response.
Purdue Model (PERA)
Enterprise Architecture Reference Model
Structural model segmenting industrial networks into hierarchical levels, from physical process equipment up to enterprise cloud connections.
EU NIS2 Directive
European Union
Mandatory regulatory framework enforcing risk management, incident reporting, and supply chain security obligations across critical infrastructure.
How to Implement ICS Security Step-by-Step
Implementing a robust industrial security posture requires a structured approach that minimizes operational risk while systematically eliminating security gaps.
Step 1: Conduct an Automated Asset Discovery and Inventory
Identify all hardware, operating software, firmware versions, and active network connections across the industrial control environment. Use passive network monitoring tools to discover field devices without generating active traffic that could disrupt sensitive control loops. Maintain an updated asset repository containing physical device locations, assigned IP addresses, and operational owners.
Step 2: Assess Cyber Risks and Prioritize Asset Criticality
Evaluate identified assets based on their operational importance, physical safety impact, and potential exposure to cyber threats. Assign criticality ratings to each component, prioritizing safety instrumented systems, primary logic controllers, and central supervisory servers. Apply vulnerability management practices to identify and prioritize unpatched software vulnerabilities, weak passwords, and unauthorized network paths.
Step 3: Implement Network Segmentation and Zoning
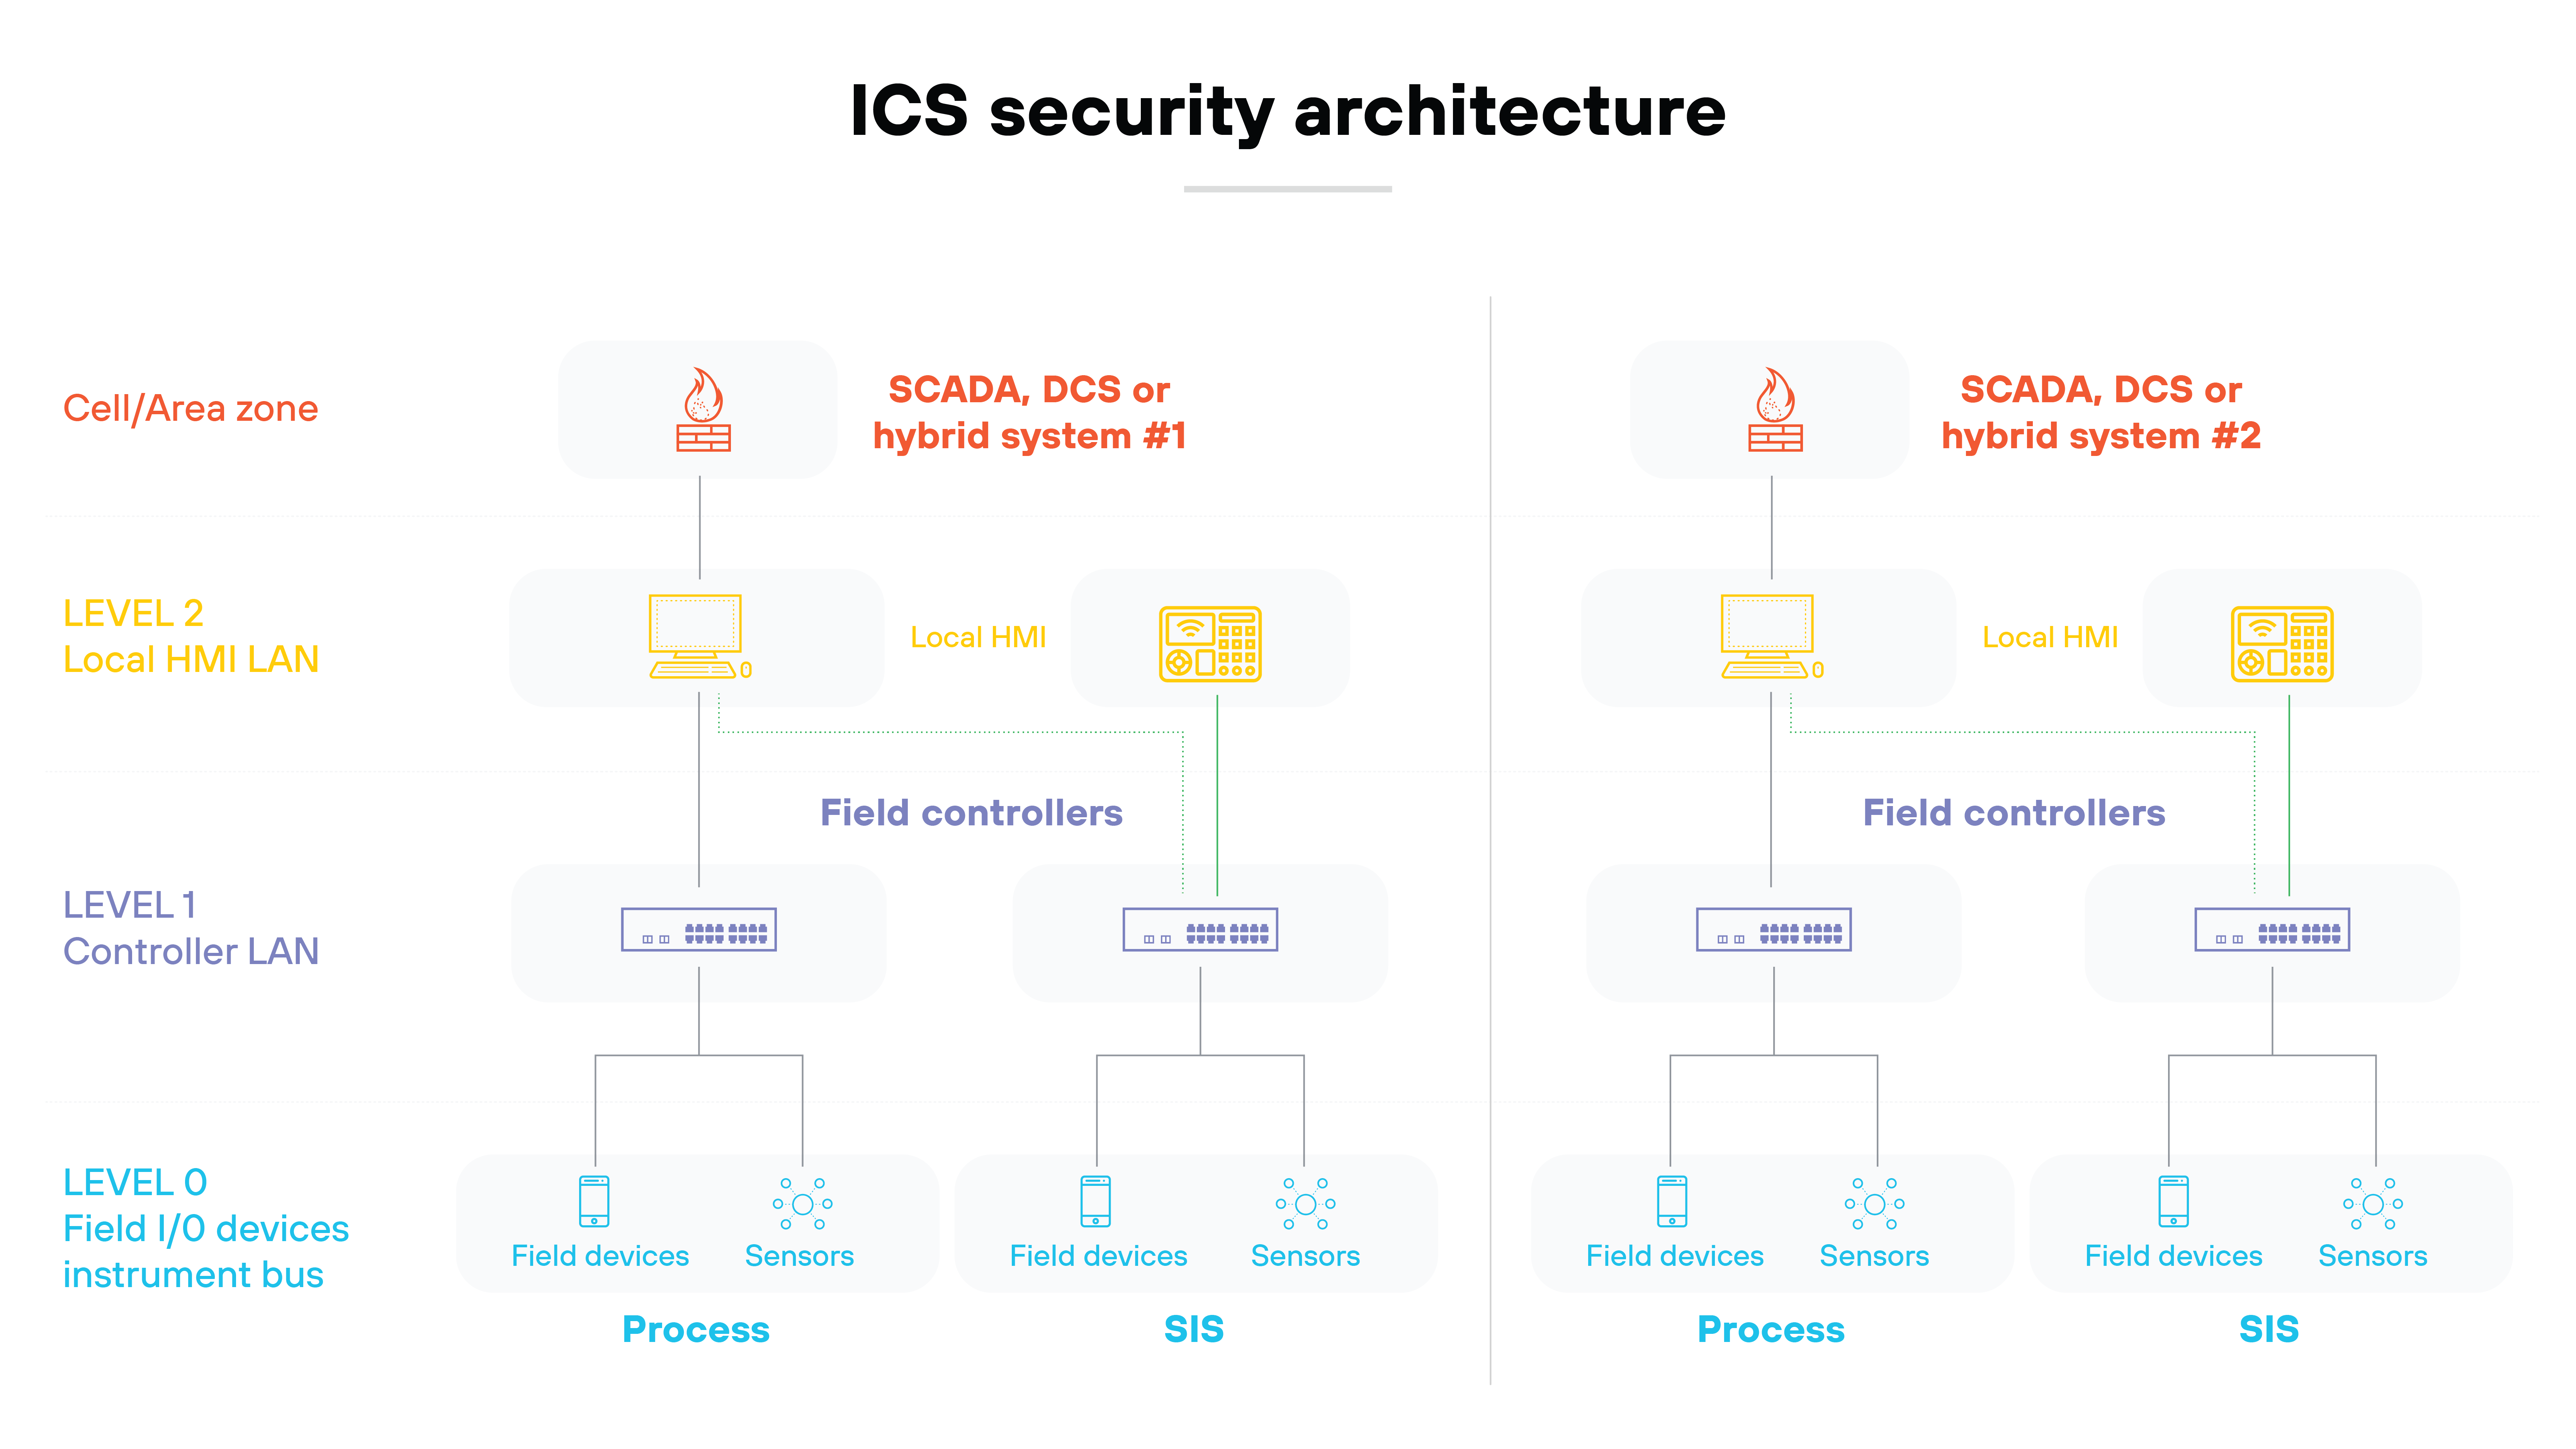
Enforce strict network segmentation by dividing industrial architectures into distinct security zones based on the Purdue Model. Isolate field-level control devices from corporate enterprise networks using dedicated industrial firewalls. Establish a segmented Industrial Demilitarized Zone (IDMZ) to handle necessary data exchanges between IT and OT systems.
Tip: Don't forget to include both internal and external threats, and factor in any human-related risks such as insider threats.
Step 4: Enforce Strict Access Controls and Least Privilege
Restrict physical and remote access to control networks based on explicit user roles and operational duties. Apply zero trust principles by requiring explicit verification and least-privilege access for administrative connections crossing into the industrial network. Strong authentication and authorization controls should include multi-factor authentication, unique individual credentials, removal of default passwords, and disabling unused network ports and services.
Step 5: Establish Virtual Patching and Vulnerability Management
Create a controlled patch management process that includes non-production testing for all security updates. When immediate software patching is not possible due to continuous production demands, deploy virtual patching via network intrusion prevention systems. Virtual patching inspects incoming traffic for known vulnerability exploits, blocking malicious packets before they reach vulnerable devices.
Step 6: Deploy Continuous Threat Monitoring and Anomaly Detection
Implement passive network monitoring platforms configured to understand specialized industrial control protocols. Establish a baseline of normal communication behavior across controllers, field devices, and management consoles. Configure real-time alerts for unexpected protocol commands, unauthorized device connections, or unusual data transfer volumes.
Tip: Ensure that your backup and recovery plans are also tested and ready to execute in the event of a compromise.
10 ICS Security Best Practices
Adopting defense-in-depth principles enables industrial organizations to maintain high operational availability while protecting critical assets from cyber threats.
Secure Physical Access: Restrict physical entry to control rooms, equipment cabinets, and network switches using biometric locks, security badges, and video surveillance.
Define Behavioral Baselines: Map normal operational traffic flows across industrial protocols to detect anomalous commands or unauthorized device behavior quickly.
Enforce Least Privilege: Limit user accounts, vendor access permissions, and application privileges to the minimum access required for specific operational duties.
Utilize Industrial Intrusion Prevention: Deploy IPS solutions trained to inspect specialized industrial protocol payloads and block known exploitation attempts in real time.
Secure Remote Connections: Require encrypted, time-limited remote access sessions protected by multi-factor authentication and explicit operator approval. Where appropriate, zero trust network access can provide policy-based access to authorized resources without broadly exposing the industrial network.
Implement Application Allowlisting: Restrict operational workstations and HMIs so that only pre-approved applications and binaries can execute.
Disable Unused Ports and Protocols: Close unnecessary physical USB ports, shut down unused network interfaces, and disable legacy services like Telnet or HTTP.
Deploy Data Diodes: Use unidirectional data diodes for sensitive security zones to permit one-way telemetry export without creating inbound attack paths.
Maintain Offline Backups: Store encrypted, regularly verified offline backups of logic controller configurations, HMI software images, and database historians.
Conduct Joint Incident Response Drills: Train cross-functional teams of IT security staff, plant engineers, and site managers using simulated industrial attack scenarios.
ICS Security FAQs
IT security focuses primarily on protecting data confidentiality and integrity across corporate networks, whereas ICS security prioritizes operational continuous availability, human worker safety, and the physical protection of machinery.
Traditional antivirus tools require frequent signature updates and run resource-intensive background scans that can consume controller CPU cycles, introduce network latency, or crash sensitive real-time control applications.
Network segmentation divides the industrial infrastructure into separate logical zones using firewalls, preventing cyber threats that breach corporate IT systems from pivoting unchecked into operational plant floors.
The Purdue Model provides a recognized hierarchical reference architecture that categorizes industrial network components into distinct functional layers, helping security teams establish clear security perimeters and access controls between physical processes and business networks.
When immediate firmware or software patching is unfeasible due to continuous operation schedules, organizations deploy virtual patching via intrusion prevention firewalls to block exploit traffic without interrupting running processes.